
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

FBI seized ‘web3adspanels.org’ hosting stolen logins

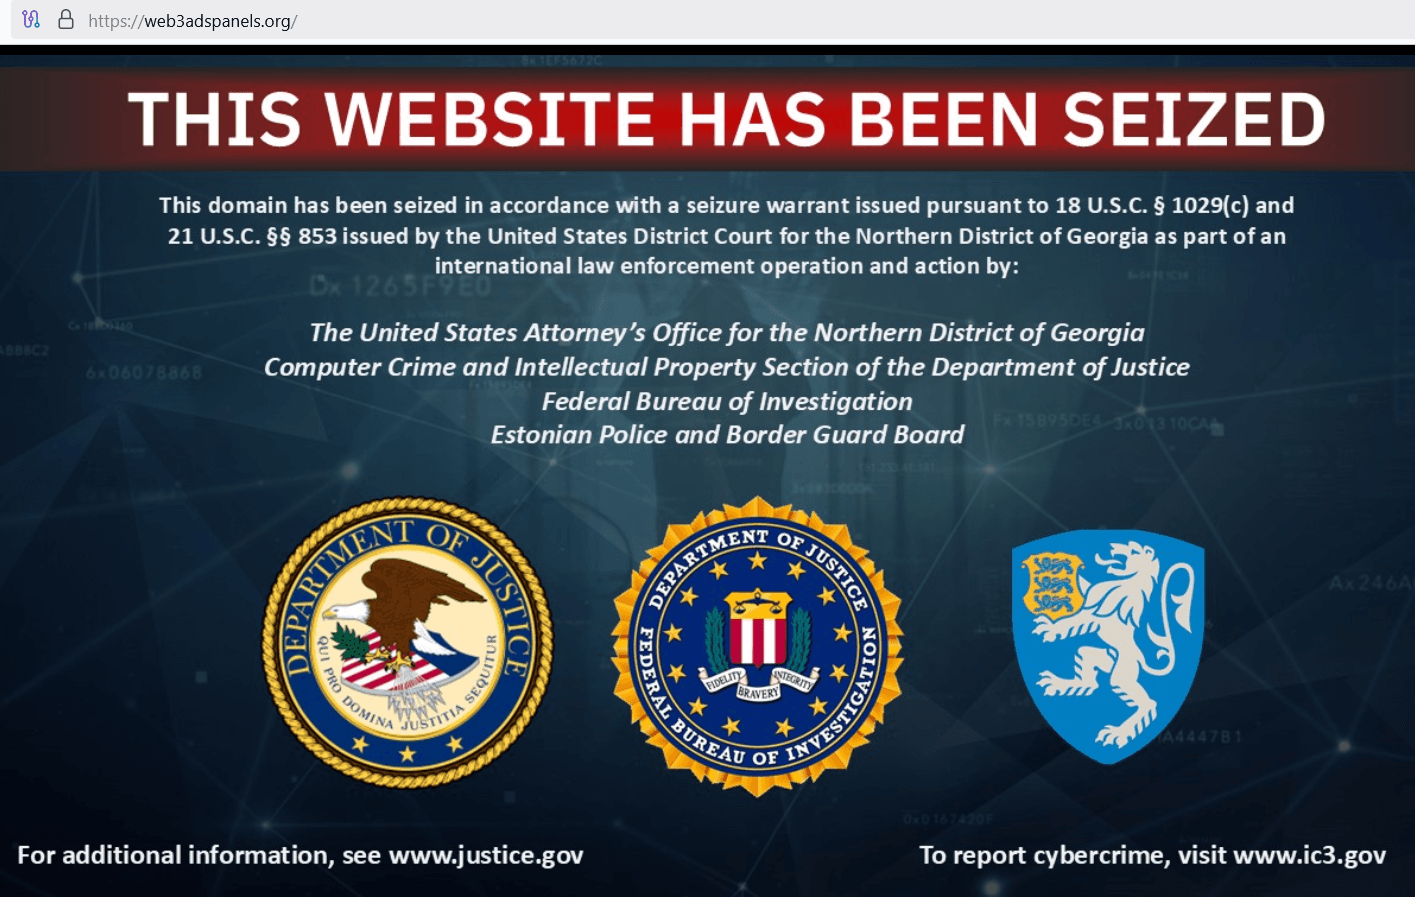
The U.S. seized the ‘web3adspanels.org’ domain and database used by cybercriminals to store stolen bank login credentials. The FBI seized the domain web3adspanels[.]org and its database after cybercriminals used it to store bank login credentials stolen from U.S. victims. A criminal group ran fake ads on Google and Bing that mimicked real bank advertisements. Victims […]

web3adspanels.org

The U.S. seized the ‘web3adspanels.org’ domain and database used by cybercriminals to store stolen bank login credentials.

The FBI seized the domain web3adspanels[.]org and its database after cybercriminals used it to store bank login credentials stolen from U.S. victims.

A criminal group ran fake ads on Google and Bing that mimicked real bank advertisements. Victims who clicked were redirected to fraudulent websites controlled by the criminals. When users entered their login credentials, malware on the fake sites captured the information. The criminals then used these stolen credentials on the real bank websites to access accounts and steal funds.

“The Justice Department today announced the seizure of a web domain and database used in furtherance of a scheme to target and defraud Americans through bank account takeover fraud. The domain, web3adspanels.org, was used by those involved in the scheme as a backend web panel to store and manipulate illegally harvested bank login credentials.” reads the press release published by DoJ. “This domain seizure comes approximately one month after the FBI issued a Public Service Announcement relating to Account Takeover Fraud via Impersonation of Financial Institution Support.”

The FBI identified at least 19 U.S. victims, including two Georgia companies, who lost about $14.6M and faced attempted losses of $28M due to a bank account takeover scheme.

The authorities seized the domain ‘web3adspanels[.]org, which was hosting thousands of stolen login credentials, and continued operating as recently as November 2025.

Estonian authorities preserved and collected data from servers hosting phishing pages and stolen login credentials used in the scheme.

Since January, the FBI’s IC3 received over 5,100 complaints, totaling more than $262M in losses. The seizure prevents criminals from using the stolen data. Estonian authorities also preserved evidence from the servers. Law enforcement officials announced the operation and urged the public to stay vigilant against phishing and monitor accounts carefully.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, web3adspanels.org)


