
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

FinCEN data shows $4.5B in ransomware payments, record spike in 2023

Ransomware payments reported to FinCEN exceeded $4.5B by 2024, with 2023 marking a record year at $1.1B across 1,512 incidents. FinCEN analyzed ransomware trends using Bank Secrecy Act (BSA) reports filed from January 2022 to February 2025. During this period, organizations reported 4,194 ransomware incidents and more than $2.1 billion in payments. For comparison, from […]

FinCEN ransomware

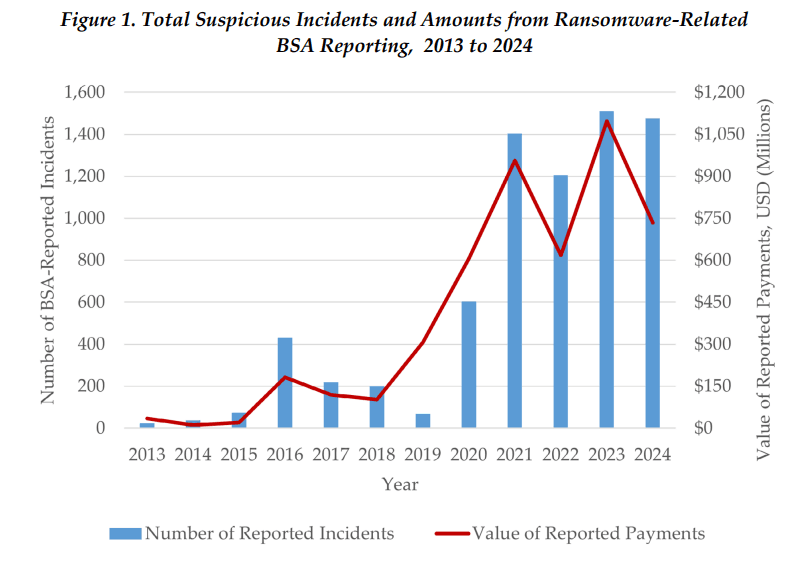
Ransomware payments reported to FinCEN exceeded $4.5B by 2024, with 2023 marking a record year at $1.1B across 1,512 incidents.

FinCEN analyzed ransomware trends using Bank Secrecy Act (BSA) reports filed from January 2022 to February 2025. During this period, organizations reported 4,194 ransomware incidents and more than $2.1 billion in payments. For comparison, from 2013 to 2021, FinCEN logged 3,075 reports totaling about $2.4 billion. Ransomware peaked in 2023 with 1,512 incidents and $1.1 billion paid, up 77% from 2022. In 2024, incidents dipped to 1,476 and payments dropped to about $734 million.

ransomware

Median ransomware payments shifted over the period: $124,097 in 2022, $175,000 in 2023, and $155,257 in 2024, with most payments under $250,000. Financial services, manufacturing, and healthcare faced the most incidents and highest total losses.

FinCEN identified 267 ransomware variants, with ALPHV/BlackCat, Akira, LockBit, Phobos, and Black Basta leading.

“Akira had the highest number of incidents (376) and ALPHV/BlackCat had the highest total
dollar value of transactions (approximately $395.3 million) during the review period, according to
FinCEN’s analysis of reported ransomware-related transactions.” reads the report.

ransomware
ransomware

According to the report, TOR was the top communication channel (67%), followed by email (28%). Nearly all payments (97%) are made in Bitcoin. Threat actors laundered funds mainly through unhosted crypto wallets and CVC exchanges.

“ransomware is a complex cybersecurity problem requiring a variety of preventive, protective, and preparatory best practices. CISA’s StopRansomware.gov offers a one-stop-shop for government resources containing alerts, guides, fact sheets, and training all focused on reducing the risk of ransomware.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


