
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Fintech firm Figure disclosed data breach after employee phishing attack

Fintech firm Figure confirmed a data breach after hackers used social engineering to trick an employee and steal a limited number of files. Blockchain-based lending firm Figure confirmed a data breach after an employee fell victim to a social engineering attack. According to a company spokesperson, the incident allowed hackers to access and steal a […]

Figure Shinyhunters

Fintech firm Figure confirmed a data breach after hackers used social engineering to trick an employee and steal a limited number of files.

Blockchain-based lending firm Figure confirmed a data breach after an employee fell victim to a social engineering attack. According to a company spokesperson, the incident allowed hackers to access and steal a limited number of files. The company disclosed the breach following inquiries and is assessing the impact.

Figure Technology Solutions, Inc. is a US financial technology company. Established in 2018, it develops and operates blockchain-based platforms used in lending, capital markets, and asset management.

The company offers consumer and institutional lending products such as HELOCs, cash-out refinancing, DSCR loans, crypto-backed loans, and operates the Figure Connect credit marketplace.

On Friday, Figure spokesperson Alethea Jadick told TechCrunch that the security breach occurred after an employee was tricked in a social engineering attack, allowing hackers to steal “a limited number of files.” She said the company is communicating “with partners and those impacted” and offering free credit monitoring “to all individuals who receive a notice.”

Figure has started notifying affected individuals and is offering free credit monitoring to those who receive a breach notice. The company has not shared the number of impacted users or when the breach was discovered.

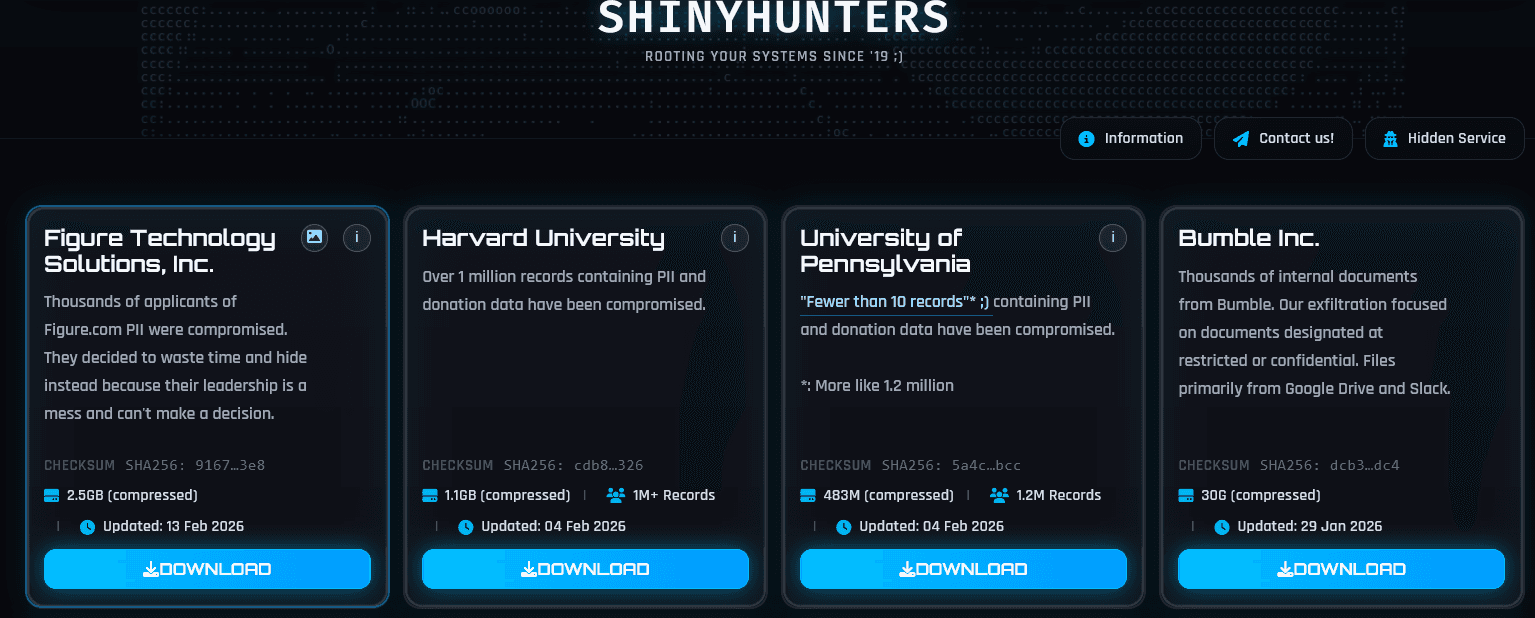
The cybercrime group ShinyHunters claimed responsibility for the breach on its dark web site, saying Figure refused to pay a ransom and releasing about 2.5GB of stolen data.

TechCrunch reviewed samples showing names, addresses, birth dates, and phone numbers, raising risks of identity fraud and phishing.

“A member of ShinyHunters told TechCrunch that Figure was among the victims of a hacking campaign that targeted customers who rely on the single sign-on provider Okta.” reported TechCruch.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)


