
The expert Kristian Erik Hermansen disclosed a zero-day flaw in the FireEye core appliance that could be exploited to gain remote root file system access.
Yesterday security researcher Kristian Erik Hermansen disclosed a zero-day vulnerability in the FireEye core appliance that could be exploited to gain remote root file system access.
Hermansen told to CSOonline that he was working with the colleague Ron Perris when discovered thirty vulnerabilities in FireEye’s product, including multiple remote root issues.
The expert also published a proof of concept to show hot to trigger the vulnerability to ccopy the /etc/passwd file.
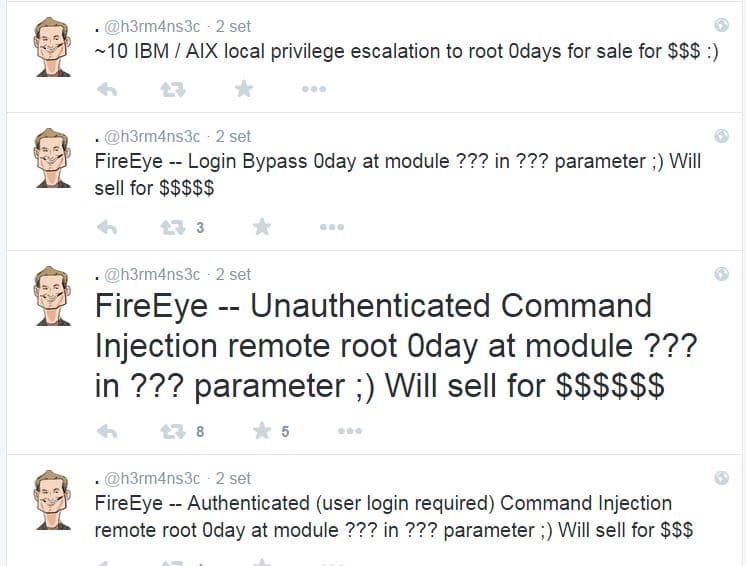
Here starts the bad news for FireEye because Hermansen claims to have discovered other three zero-day and is offering them for sale. Hermansen claims to have found a login bypass vulnerability, a command injection vulnerabilities.

The disclosed flaw seems to affect a PHP script on the FireEye appliance, the expert has publicly criticized the implementation of the popular security firm.
“FireEye appliance, unauthorized remote root file system access. Oh cool, web server runs as root! Now that’s excellent security from a _security_ vendor 🙂 Why would you trust these people to have this device on your network,” wrote Hermansen in a note.
“Just one of many handfuls of FireEye / Mandiant 0day. Been sitting on this for more than 18 months with no fix from those security “experts” at FireEye. Pretty sure Mandiant staff coded this and other bugs into the products. Even more sad, FireEye has no external security researcher reporting process.”
Hermansen posted the PoC for the FireEye remote root file system access 0-day on Pastebin, he is offering the other vulnerabilities for sale and the base asking price starts at around $10,000 USD per bug.
“I tried for 18 months to work with FireEye through responsible channels and they balked every time. These issues need to be released because the platforms are wrought with vulnerabilities and the community needs to know, especially since these are Gov-approved Safe Harbor devices with glaring remote root vulnerabilities,” Hermansen told Salted Hash via email.
“No one should be trusting these devices on their network if FireEye can’t be bothered to fix the problems. As a security company, their standards should be higher.”
Hermansen made headlines after he disclosed a number of security issues with the Covered California website as reported by Forbes:
“Hermansen discovered a vulnerability that would allow someone to take over another person’s account on the California site, and review or change the information entered there. He tried contacting Covered California “at least 15 times” by email, phone or chat about the problem, but got no response for over a month. “They must have been overwhelmed by people seeking help with the site,” he said.”
Stay Tuned …
(Security Affairs – FireEye, hacking)


