
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Microsoft warns of attacks delivering FlawedAmmyy RAT directly in memory

Researchers at Microsoft uncovered a malicious campaign that delivers the infamous FlawedAmmyy RAT directly in memory. Experts at Microsoft uncovered a malicious campaign that delivers the FlawedAmmyy RAT directly in memory. The FlawedAMMYY backdoor borrows the code of the Ammyy Admin remote access Trojan, it allows attackers to get full access to a victim’s machine. […]

FlawedAmmyy RAT

Researchers at Microsoft uncovered a malicious campaign that delivers the infamous FlawedAmmyy RAT directly in memory.

Experts at Microsoft uncovered a malicious campaign that delivers the FlawedAmmyy RAT directly in memory.

The FlawedAMMYY backdoor borrows the code of the Ammyy Admin remote access Trojan, it allows attackers to get full access to a victim’s machine. FlawedAmmyy RAT allows stealing sensitive data from infected systems and exfiltrating files.

FlawedAmmyy Remote Access Trojan was involved in attacks carried out by the threat actors tracked as TA505.

Microsoft observed weaponized spam messages using .xls attachments with content in Korean. The macro included in the documents executes the legitimate msiexec.exe tool that downloads an MSI archive.

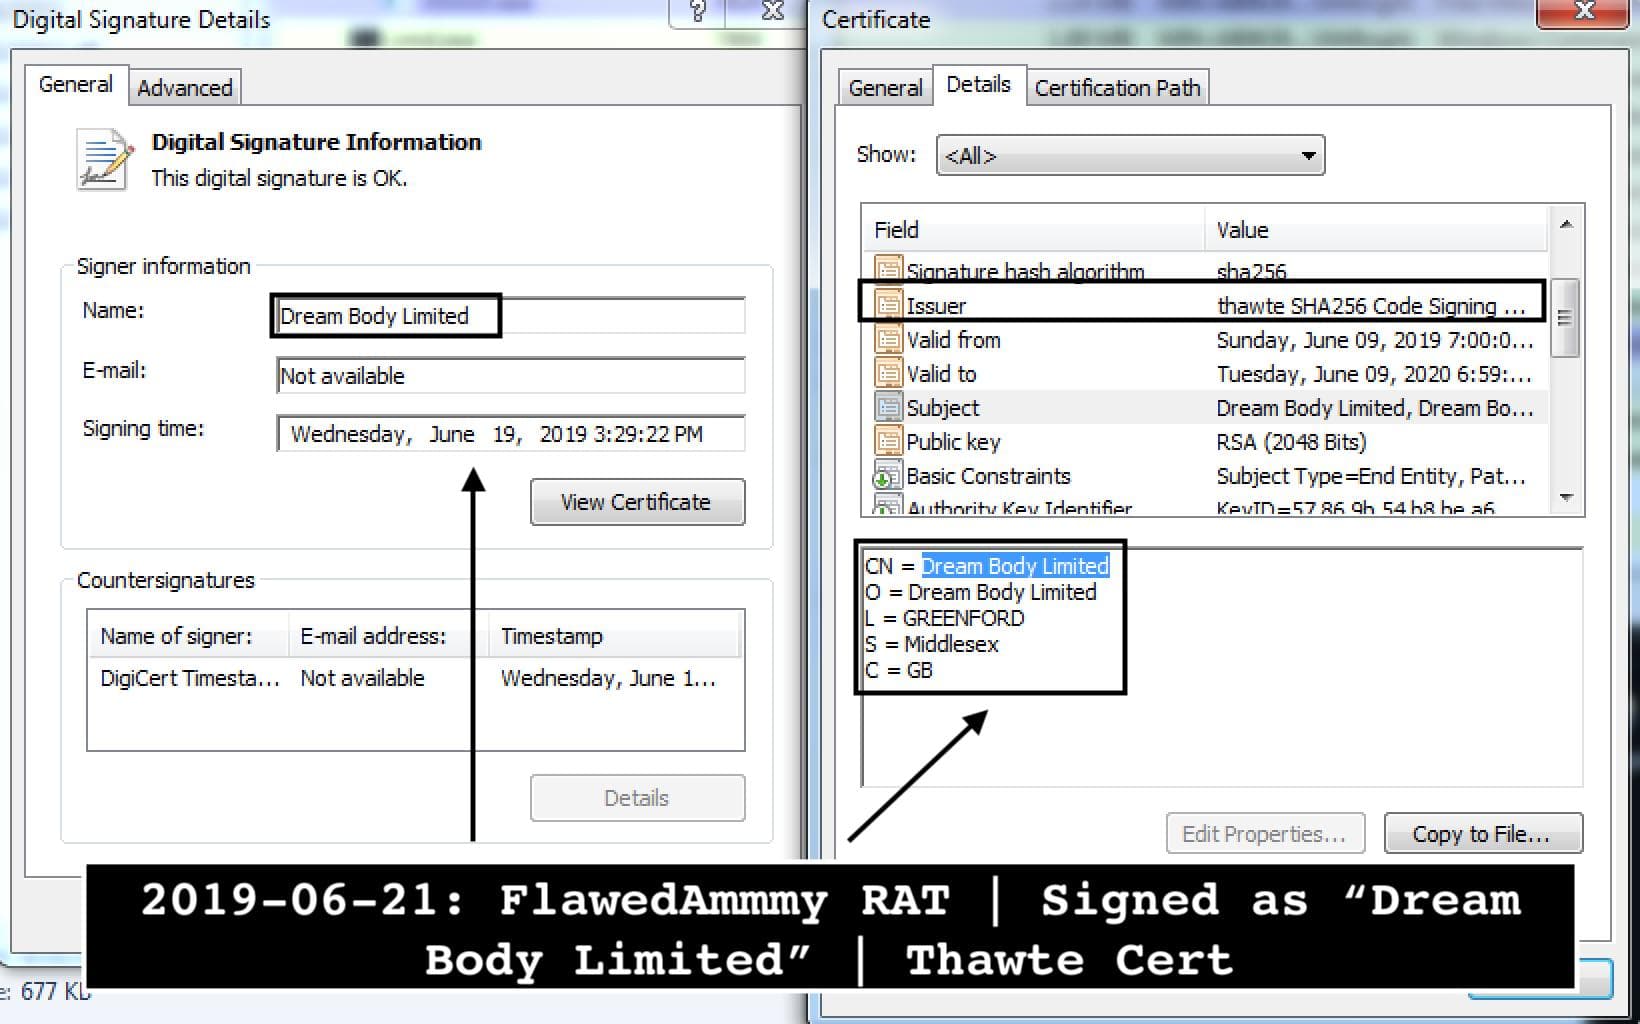
The MSI archive includes a digitally signed executable that decrypts and execute another executable in memory once it is opened.

“This executable then downloads and decrypts another file, wsus.exe, which was also digitally signed on June 19. wsus.exe decrypts and runs the final payload directly in memory. The final payload is the remote access Trojan FlawedAmmyy,” reads a Tweet published by Microsoft Security Intelligence.

One of the samples involved in this campaign, detected on June 22, was digitally signed using a certificate issued by Thawte for Dream Body Limited.

FlawedAmmyy RAT

In May, experts at Yoroi-Cybaze Z-Lab observed a spike in the number of attacks against the banking sector and spotted a new email stealer used by the TA505 hacker group.

Earlier June, researchers at Trend Micro observed the TA505 group carrying out attacks, involving the FlawedAmmyy RAT and other RATs, against users in Latin America and Asia.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – FlawedAmmyy, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


