
Security Affairs
U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A man who goes by the nickname LiquidWorm released a FLIR Thermal Camera Exploit

On September 25, 2017, a man which goes by the nickname ‘LiquidWorm’ has released the exploit code for FLIR Thermal Cameras. On 2017-09-25 another CCTV exploit got release by a man which goes by the nickname ‘LiquidWorm’. He found out that FLIR CCTV ’s by the vendor “FLIR Systems” had a hard-coded ssh login credentials […]

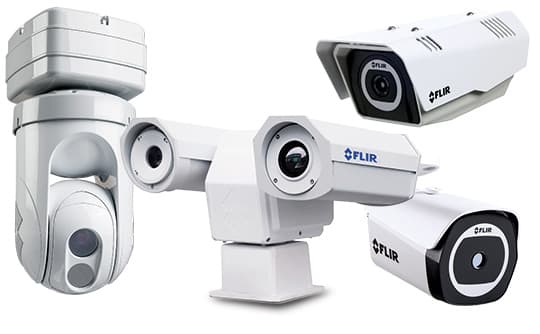
FLIR CCTV Thermal Camera

On September 25, 2017, a man which goes by the nickname ‘LiquidWorm’ has released the exploit code for FLIR Thermal Cameras.

On 2017-09-25 another CCTV exploit got release by a man which goes by the nickname ‘LiquidWorm’. He found out that FLIR CCTV ’s by the vendor “FLIR Systems” had a hard-coded ssh login credentials within its Linux distribution image, Those credentials are never exposed to the end user and CANNOT be changed through any normal operation of the camera.

FLIR CCTV Thermal Camera

What kind of exploit is this?

This exploit is what we know as a “Backdoor” because it grants Randoms access to the camera’s, and even allows them to download code, or do worse.

What are the Affected version?

So far camera models of F/FC/PT/D Software version 10.0.2.43 and Firmware version: 8.0.0.64 release: 1.4.1, 1.4, 1.3.4 GA, 1.3.3 GA and 1.3.2 are affected by the exploit.

What kind of cameras are those? The FLIR cameras are high-performance, multi-sensor pan/tilt cameras which bring thermal and visible-light imaging together in a system that gives you video and control over both IP and analog networks.

Is this exploit fixable by the end user itself?

No, after testing around with a test model, there isn’t any way of removing the hard-coded ssh login credentials, the vendor itself would have to remove the SSH login credentials from the code.

Is this exploit critical?

Yes, these kinds of exploits are unnecessary and not needed, Since Random people can now scan for affected versions and most likely infect them, the rate of IoT botnets will rise again, which is a bad thing.

What to do?

The only thing the affected camera owners can do is wait until the Vendor releases a patch which removes the hard-coded ssh login of the Linux distribution image.

Thank you for reading.

Report written by Frontline Cyber Security Ltd

Newark On Trent

About the author: Frontline Cyber Security Ltd

Company Registration Number 10803746 Newark

Nottinghamshire – United Kingdom

contact@frontlinecybersecurity.com

https://frontlinecybersecurity.com

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – FLIR Thermal Camera Exploit, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


