
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Ford data breach involved a third-party supplier

Ford investigates a data breach linked to a third-party supplier and pointed out that its systems and customer data were not compromised. Ford investigation investigated a data breach after a threat actors claimed the theft of customer information on the BreachForums cybercrime. On November 17, threat actors IntelBroker and EnergyWeaponUser published a post on BreachForums […]

Ford

Ford investigates a data breach linked to a third-party supplier and pointed out that its systems and customer data were not compromised.

Ford investigation investigated a data breach after a threat actors claimed the theft of customer information on the BreachForums cybercrime.

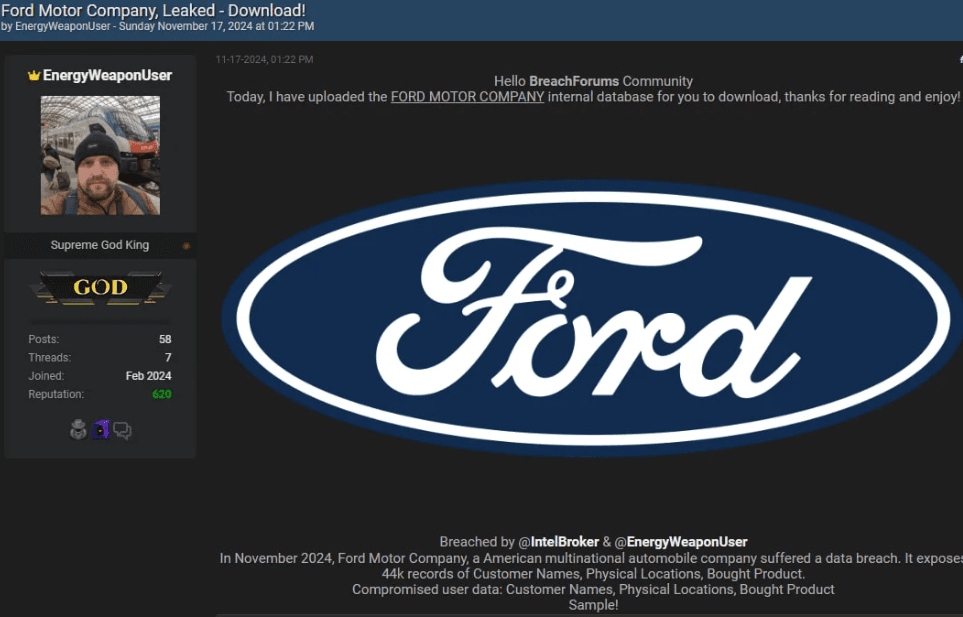
On November 17, threat actors IntelBroker and EnergyWeaponUser published a post on BreachForums announcing they have stolen 44,000 Ford customer records.

Below is the announcement published by the duo on the cybercrime forum:

Ford

“Breached by @IntelBroker & @EnergyWeaponUser

In November 2024, Ford Motor Company, an American multinational automobile company, suffered a data breach. It exposed 44k records of Customer Names, Physical Locations, Bought Product.

Compromised user data: Customer Names, Physical Locations, Bought Product”

Compromised data include names, physical addresses, and purchase info.  

Ford provided the following statement to the media [1,2], it confirmed that threat actors did not hack its systems.

“Ford’s investigation has determined that there was no breach of Ford’s systems or customer data. The matter involved a third-party supplier and a small batch of publicly available dealers’ business addresses. It is our understanding that the matter has now been resolved.”a Ford spokesperson told media.

IntelBroker is known to have stolen data from multiple high-profile organizations, including Cisco, Europol, DC Health Link, Volvo Cars, and HPE.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)


