Security Affairs
Predator, Pegasus and Graphite: Governments Accused of Spyware Abuse Face Little Accountability|Zoom Fixes Critical Windows Vulnerability Allowing Privilege Escalation|Poland takes its national e-government platform offline after a cyberattack|AI Pentest Tool AntiFox Abused To Steal AWS Credentials|WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data|Hackers Advertise a $1,000 Gmail Tool That Allegedly Survives Password Resets|Microsoft November Patch Tuesday: one exploited Outlook bug and 30 wormable flaws|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|Predator, Pegasus and Graphite: Governments Accused of Spyware Abuse Face Little Accountability|Zoom Fixes Critical Windows Vulnerability Allowing Privilege Escalation|Poland takes its national e-government platform offline after a cyberattack|AI Pentest Tool AntiFox Abused To Steal AWS Credentials|WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data|Hackers Advertise a $1,000 Gmail Tool That Allegedly Survives Password Resets|Microsoft November Patch Tuesday: one exploited Outlook bug and 30 wormable flaws|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

PoC exploit for critical RCE flaw in Fortra FileCatalyst transfer tool released

Fortra addressed a critical remote code execution vulnerability impacting its FileCatalyst file transfer product. Fortra has released updates to address a critical vulnerability, tracked as CVE-2024-25153 (CVSS score 9.8) impacting its FileCatalyst file transfer solution. A remote, unauthenticated attacker can exploit their vulnerability to execute arbitrary code on impacted servers. “A directory traversal within the ‘ftpservlet’ of the FileCatalyst […]

fortra filecatalyst

Fortra addressed a critical remote code execution vulnerability impacting its FileCatalyst file transfer product.

Fortra has released updates to address a critical vulnerability, tracked as CVE-2024-25153 (CVSS score 9.8) impacting its FileCatalyst file transfer solution.

A remote, unauthenticated attacker can exploit their vulnerability to execute arbitrary code on impacted servers.

“A directory traversal within the ‘ftpservlet’ of the FileCatalyst Workflow Web Portal allows files to be uploaded outside of the intended ‘uploadtemp’ directory with a specially crafted POST request.” reads the advisory. “In situations where a file is successfully uploaded to web portal’s DocumentRoot, specially crafted JSP files could be used to execute code, including web shells.”

According to the advisory, the vulnerability was reported in August 2023 by Tom Wedgbury from LRQA Nettitude, before Fortra joining the CNA program and the company fixed it in August 2023.

“We are issuing a CVE now at the request of the individual who initially reported the vulnerability” continues the advisory.

The vulnerability was fixed with the release of FileCatalyst Workflow version 5.1.6 Build 114.

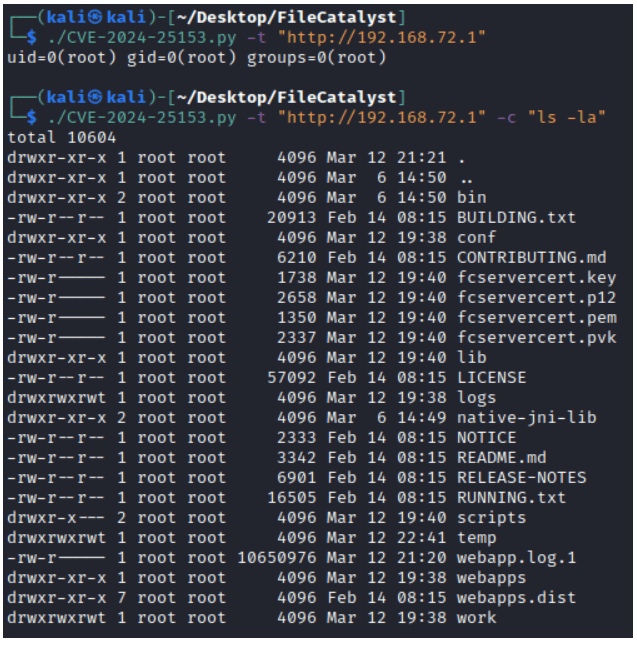
Researchers from Nettitude released on GitHub a full proof-of-concept exploit for this vulnerability. The PoC exploit demonstrates how to upload a web shell on vulnerable instances to execute operating system commands.

The exploit will:

  1. Automatically detect whether anonymous login is enabled.
  2. Get a valid session token.
  3. Upload a command shell with a pseudo-randomly generated file name.
  4. Execute the OS command.

With previously disclosed flaws in Fortra GoAnywhere managed file transfer (MFT) coming under heavy exploitation last year by threat actors like Cl0p, it’s recommended that users have applied the necessary updates to mitigate potential threats.

fortra filecatalyst

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Fortra Filecatalyst)