
Foxit Software, the company behind the Foxit PDF reader app, disclosed a data breach that exposed customers’ information, including passwords.
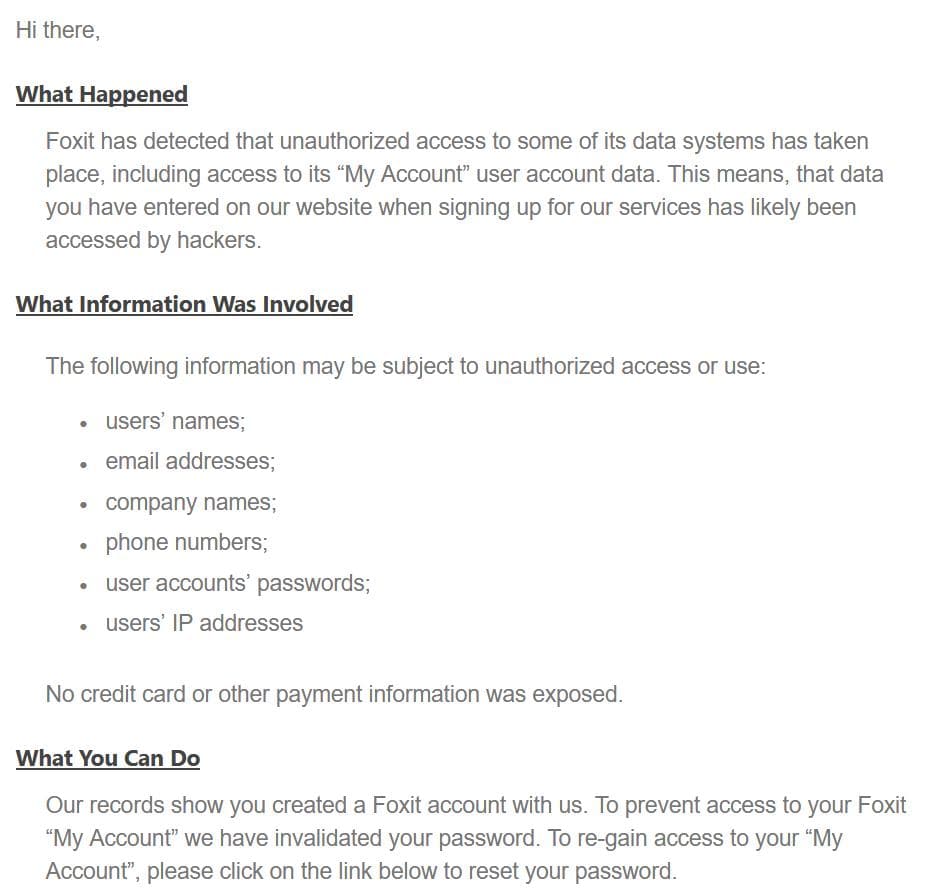
Foxit Software, the PDF software provider behind the Foxit PDF reader app disclosed a security breach that took place recently exposing customers’ information. The incident exposed personal identification data of ‘My Account’ service users, third parties accessed to client’s information such as email addresses, passwords, real names, phone numbers, company names, and IP addresses from which users logged into their accounts.
According to the Foxit, the company has over 525 million users worldwide.
“Foxit has determined that unauthorized access to its data systems took place recently. Third parties have gained access to Foxit’s ‘My Account’ user account data, which contains email addresses, passwords, users’ names, phone numbers, company names and IP addresses,” reads a security advisory published by the company.
The free membership ‘My Account’ service provides customers with access to “software trial downloads, order histories, product registration information, and troubleshooting and support information,” this means that no financial data was
Foxit pointed out that it does not maintain customer payment card information in its systems.
Foxit already notified the impacted ‘My Account’ users of the security breach via emails and forced them to reset passwords.
The company reported the incident to law enforcement and is investigating the incident with the help of a security management firm
“Foxit’s security team has immediately launched a digital forensics investigation. The company has invalidated the account passwords for all potentially impacted accounts, requiring users to reset their passwords to regain access to the My Account service. Foxit has notified law enforcement agencies and data protection authorities and is destined to cooperate with the agencies’ investigations.” continues the advisory. “In addition, the company has hired a security management firm to conduct an in-depth analysis, strengthen the company’s security posture and protect against future cyber security incidents.”

The data breach notification emails don’t clarify the way Foxit had protected customer passwords, it could be interesting to know if the company has used hashing and salting
The company
“Foxit also recommends customers to remain vigilant by reviewing account statements and monitoring credit reports to avoid identity theft. Customers should furthermore be aware that fraudsters may use their data to gather further information by deception (“phishing”).” concludes the advisory. “Security and the privacy of customer data is very important to Foxit, and the company will take all reasonable steps to ensure customer information stay secure in the future.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(
[adrotate banner=”5″]
[adrotate banner=”13″]


