
Cyber security expert and founder of Yoroi has published a new tool that could be used to spot APTs (Advanced Persistent Threats) through Malware streams.
There are many ways to spot Advanced Persistent Threats, for example during a forensic analysis on “high rate incident” or having sandbox systems on critical infrastructures or again working as incident responder for big companies, working into a national CERT or building a simple tool performing analysis on Malware streams. Today I’d like to share a little bit of my personal experience on spotting APTs through Malware streams.
First of all, let me say that it is the easiest way to spot APT groups but it’s also one of the most inaccurate and it needs a lot of manual analysis before being able to confirm the sample belongs to a specific APT. Having said that, you might decide to get a Malware streaming service (or you might build one on your own, this was my case) and decide to perform dynamic or static analysis on it.
A few years ago when I approached this problem I decided (in the first stage) to exploit static analysis and to build up specific signatures to detect possible APTs on a given Malware stream. So let’s say I do have a personal Malware stream and I do have a personal engine who is able to perform basic static analysis (by comparing YARA rules) over and over again on a given Malware stream, so why don’t write specific signature for APTs and manually check every single output to see for false positives or real APTs?

So I wrote it up and today after few years I decided to share it with all of my readers ! I hope you might find interesting samples to start analysis and to find nice and interesting samples.Please if you find it useful help me in sharing it by linking HERE so that many cybersecurity analysts might decide to start from here to investigate new samples.
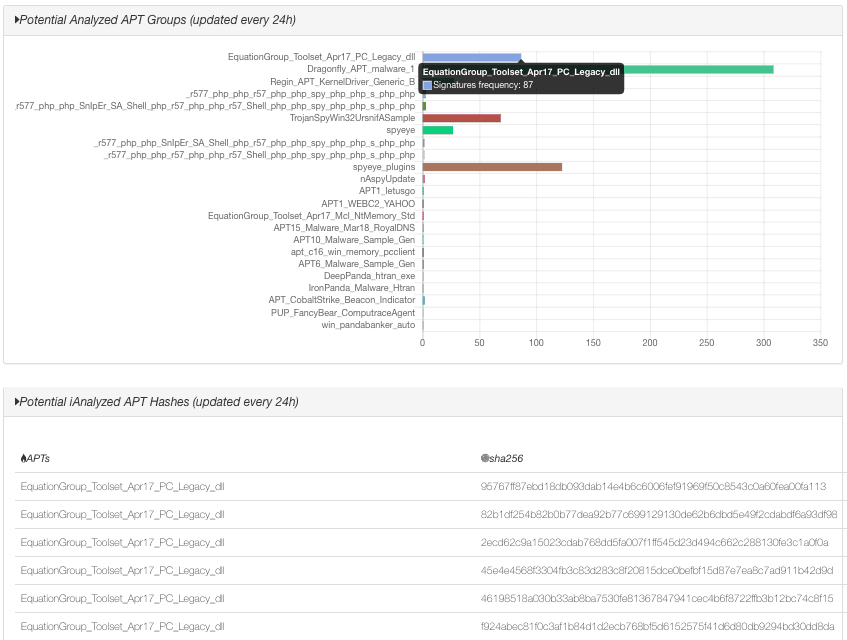
According to the static analysis, we might build YARA rules to identify a specific set of binaries. If we classify those binaries as “related to APT” we might extract from tons of binaries the ones that match classified YARA rules and that could be related to APTs. So here we are! The following table represents a set of binaries which hit classified YARA rules related to APTs. Of course, we might have false positives for mainly two reasons: (i) It’s only static analysis. If you run those Samples on live SandBox you might discover unattended behavior. (ii) No human analysis.
This is the result of mere algorithms, no human interacted and checked those results.
Marco Ramilli also published other free tools:
- The Malware Hunter tool, a simple but interesting catching tool based on static YARA rules.
- Honey Feed, a tool that extracts suspicious IPs from undesired connections, his
HoneyPots . - A simple tool for
malware static analysis he used to perform massive Malware analysis research.
Below the original post published by Marco Ramilli:
About the author: Marco Ramilli, Founder of Yoroi

I am a computer security scientist with an intensive hacking background. I do have a MD in computer engineering and a PhD on computer security from University of Bologna. During my PhD program I worked for US Government (@ National Institute of Standards and Technology, Security Division) where I did intensive researches in Malware evasion techniques and penetration testing of electronic voting systems.

I do have experience on security testing since I have been performing penetration testing on several US electronic voting systems. I’ve also been encharged of testing uVote voting system from the Italian Minister of homeland security. I met Palantir Technologies where I was introduced to the Intelligence Ecosystem. I decided to amplify my cybersecurity experiences by diving into SCADA security issues with some of the biggest industrial aglomerates in Italy. I finally decided to found Yoroi: an innovative Managed Cyber Security Service Provider developing some of the most amazing cybersecurity defence center I’ve ever experienced! Now I technically lead Yoroi defending our customers strongly believing in: Defence Belongs To Humans
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(
[adrotate banner=”5″]
[adrotate banner=”13″]


