
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Registral Function of the State Mexico (FREM) hacked. Shad0wS3C is back

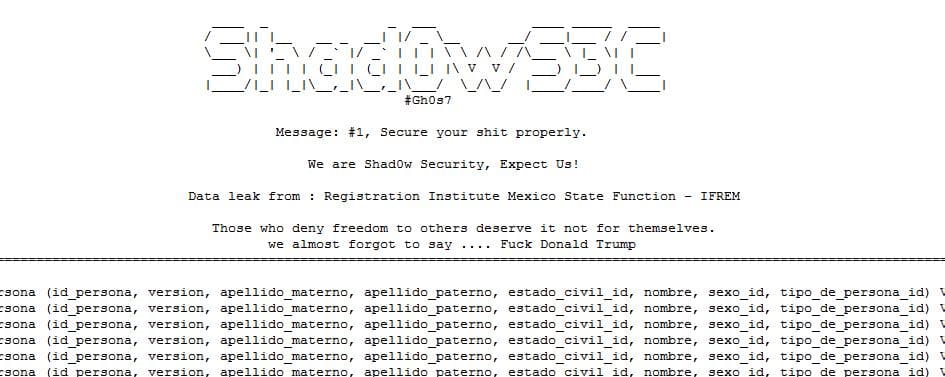
The hacker group Shad0wS3C is back and hacked the Institute of the Registral Function of the State Mexico (FREM), it leaked the database. Shad0wS3C is Back and hacked the Institute of the Registral Function of the State Mexico (FREM) and leaked a dump of its database. The hacker leaked the database at the following URL https://t.co/6XgwSf4uWW The […]

Registral Function of the State Mexico (FREM) hacked. Shad0wS3C is back

The hacker group Shad0wS3C is back and hacked the Institute of the Registral Function of the State Mexico (FREM), it leaked the database.

Shad0wS3C is Back and hacked the Institute of the Registral Function of the State Mexico (FREM) and leaked a dump of its database.

The hacker leaked the database at the following URL

https://t.co/6XgwSf4uWW

frem-mexico-data-breach

The archive includes three files containing personal information of the users, including passport info and other sensitive details.

In the past, Shad0wS3C was an hacktivist group, it seems to have changed its mission and started hacking without any specific political motivation.

Its member Gh0s7, told me that the FREM data breach is just an anticipation of future attacks.

“This leak is just a simple demonstration for our future attacks. We will be leaking more gov and private corps.” Gh0s7 told me.

The group launched a targeted attack, the first of a new wave that aims to hit government servers and corporations worldwide.

The hackers have a list of targets composed of gov and private servers to hack.

This is their “black list.”

Hackers did not reveal details of the data breach, they simply told me to have used a “private exploit.”

The last time hack in order of time made by Shad0wS3C is the Paraguay’s Secretary of National Emergency (SNE) data breach occurred in August. The hackers leaked online a dump from a PostgreSQL database also in this case.

Stay Tuned.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Gh0s7, FREM)


