
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

French aircraft carrier Charles de Gaulle tracked via Strava activity in OPSEC failure

A French aircraft carrier was tracked in real time via a sailor’s Strava activity, exposing a persistent operational security flaw. Le Monde revealed that France’s aircraft carrier Charles de Gaulle was tracked in real time through an officer’s activity on the Strava app. A sailor unknowingly shared running data from the ship, exposing its location […]

aircraft carrier Charles de Gaulle position leak

A French aircraft carrier was tracked in real time via a sailor’s Strava activity, exposing a persistent operational security flaw.

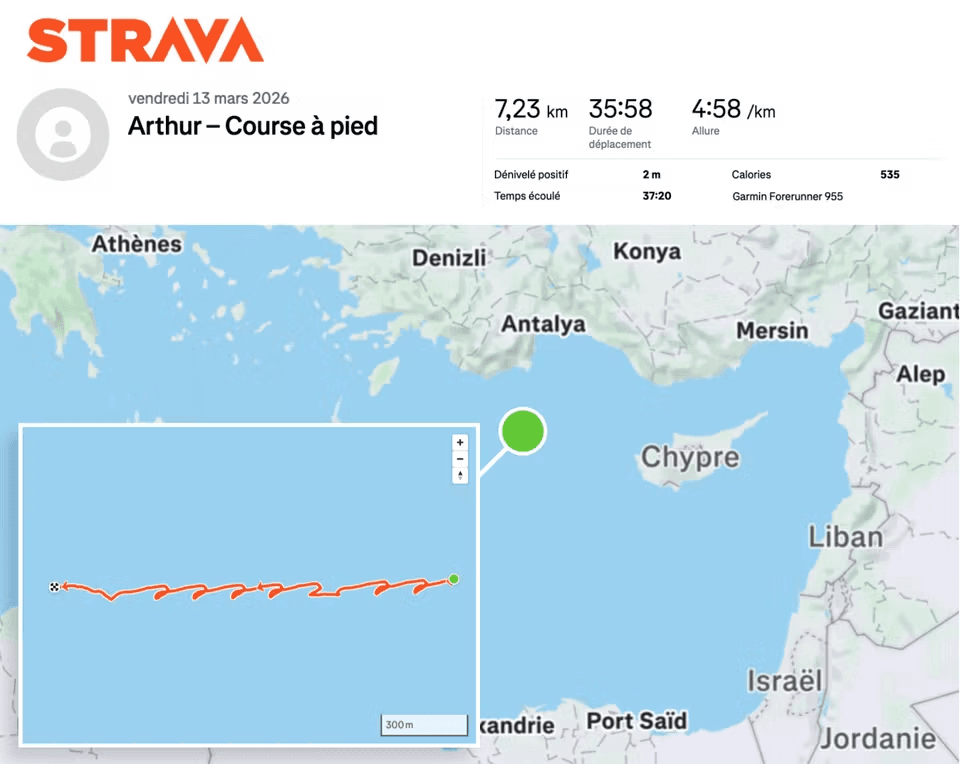
Le Monde revealed that France’s aircraft carrier Charles de Gaulle was tracked in real time through an officer’s activity on the Strava app. A sailor unknowingly shared running data from the ship, exposing its location in the Mediterranean. The French sailor’s public Strava profile, set as “public,” revealed the near real-time location of the aircraft carrier in the Mediterranean, near Cyprus and Turkey.

“On March 13, at 10:35 a.m., amidst the waves, Arthur (not his real name), a young officer in the French Navy, was out for a run, circling the deck of the ship where he worked. To record his performance—a little over 7 kilometers covered in thirty-five minutes—he used the smartwatch on his wrist. The data collected was then uploaded to the internet.” reported the French media outlet Le Monde. “Because Arthur has a profile on the sports app Strava, and it’s “public”: anyone can view it. “

The case highlights ongoing security risks from fitness apps, as sensitive military positions can still be revealed despite prior warnings.

aircraft carrier Charles de Gaulle position leak

President Emmanuel Macron announced the deployment of the French naval task force, including the aircraft carrier Charles de Gaulle, three frigates, and a supply ship, on March 3.

“On March 3, Emmanuel Macron himself announced that he had ordered its deployment, just days after the start of the war between Israel, the United States, and Iran.” concludes the report. “The sole French aircraft carrier was then in the Baltic Sea as part of NATO exercises and was scheduled to remain there until May. Its transit”

In the past, Strava fitness data has exposed sensitive military locations worldwide, as American and allied military personnel unknowingly shared exercise routes near bases in Afghanistan, Iraq, and Syria.

These maps clearly highlight otherwise hidden facilities and troop movements, creating serious security risks. Experts warn such data could help adversaries identify and target military sites, underscoring ongoing privacy issues with fitness trackers.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, aircraft carrier Charles de Gaulle)


