
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Google introduced G Suite alerts for state-sponsored attacks

Google announced that has implemented an alerting system for G Suite admins when users have been targeted by state-sponsored attacks. Google announced it will alert G Suite admins when state-sponsored hackers will target their users. The new feature will be available in the G Suite Admin console very soon, it confirms the effort spent by the tech […]

G Suite state sponsored attacks

Google announced that has implemented an alerting system for G Suite admins when users have been targeted by state-sponsored attacks.

Google announced it will alert G Suite admins when state-sponsored hackers will target their users.

The new feature will be available in the G Suite Admin console very soon, it confirms the effort spent by the tech giant of protecting its users.

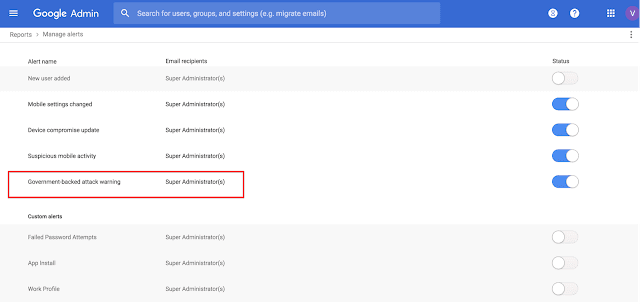
“We’re adding a feature in the Admin console that can alert admins if we believe a user’s account has been targeted by a government-backed attack. If an admin chooses to turn the feature on, an email alert (to admins) is triggered when we believe a government-backed attacker has likely attempted to access a user’s account or computer through phishing, malware, or another method.” reads the security advisory published by Google.

“It does not necessarily mean that the account has been compromised or that there was a widespread attack on an organization.” 

In June 2012, for the first time, the company announced it was going to offer a specific protection service for a restrict number of users that could be the target of state-sponsored attacks.

Google is now implementing the new protection feature within the G Suite Admin console, admins will have the opportunity to receive alerts whenever attacks could be attributed to a nation-state actor.

Every time an attack will be detected, admins can choose to secure the account hit by the hackers and can also opt to alert the victim.

The alerts don’t necessarily imply that the account has been hacked or that the organization has been compromised in a massive attack.

G Suite state sponsored attacks

Google pointed out the alerts will be turned off by default, admins can choose to turn them on in the Admin Console > Reports > Manage Alerts > Government backed attack.

According to Google, the new feature is set to gradually roll out to all G Suite editions, the tech giant plans to make it available for all admins within the next 15 days.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – G Suite alerts, state-sponsored attacks)

[adrotate banner=”5″]

[adrotate banner=”13″]


