
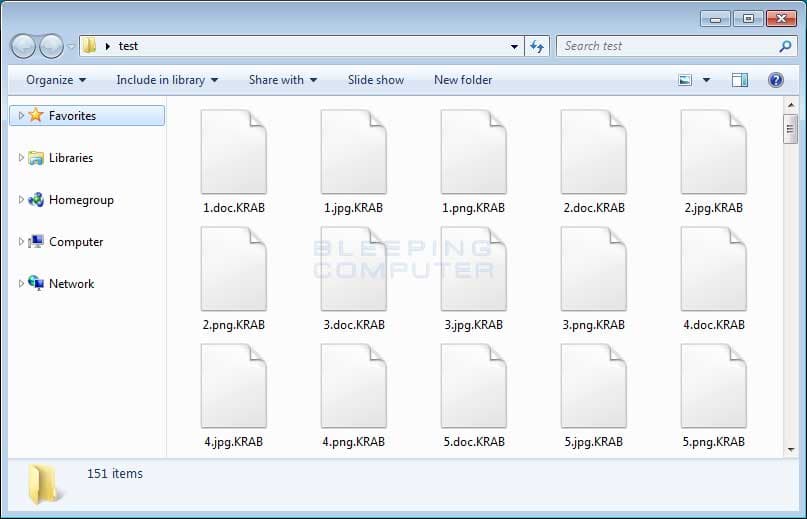
A new variant of the infamous GandCrab ransomware V4 was released during the weekend, experts shared details of the threat,
A new version of the dreaded GandCrab ransomware (V4) was released during the weekend and according to the experts it included numerous changes.
New #GandCrab version "V4" GANDCRAB V4 Ransomware – Remove and Restore .KRAB Encrypted Files https://t.co/QJJdoVl8tY
— 0x0 (@cyber0xy) July 3, 2018
The GandCrab ransomware V4 uses different encryption algorithms (likely the Salsa20 stream cipher) and a new TOR payment site (gandcrabmfe6mnef.onion), it appends the “.KRAB” extension to the encrypted file’s names and use a new ransom note name.

#GandCrab V4 internal version: 4.0 – seems to use now #Salsa20 stream cipher 🧐 pic.twitter.com/Op01bBC50g
— Marcelo Rivero (@MarceloRivero) July 3, 2018
The GandCrab authors left a message in the code for the computer science professor at the University of Illinois at Chicago Daniel J. Bernstein who created the Salsa20 algorithm.
@hashbreaker Daniel J. Bernstein let's dance salsa <3According to a malware researcher Fly, the GandCrab ransomware V4 is currently being distributed through fake software crack sites.
“The ransomware distributors will hack legitimate sites and setup fake blogs that offer software crack downloads. When a user downloads and runs these cracks, they will install the GandCrab Ransomware onto the computer.” wrote Lawrence Abrams from Bleeping Computer.
Like previous variants, when GandCrab ransomware V4 is executed it will scan the computer and network shares for files to encrypt.
Lawrence added that this variant enumerates all shares on the network and not just mapped drives. Once encrypted files, the ransomware will create ransom notes named KRAB-DECRYPT.txt that includes payment instructions. The ransom amount is currently $1,200 USD worth of DASH (DSH) cryptocurrency.

The TOR payment site includes a support section where victims can send messages to the developers and request to decrypt one file for free as the proof of their abilities.
The bad news is that, at this time, victims of GandCrab ransomware v4 cannot decrypt their files for free.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – malware, GandCrab ransomware v4)
[adrotate banner=”5″]
[adrotate banner=”13″]


