
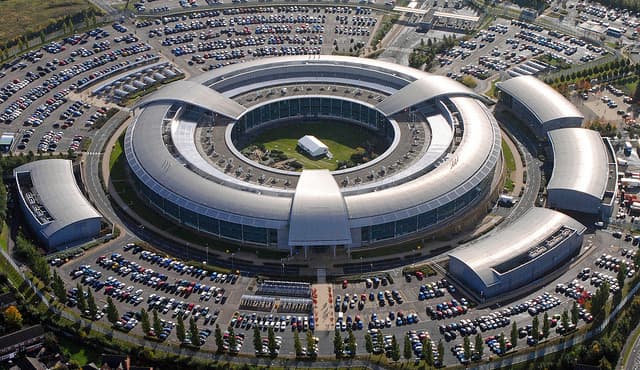
New documents leaked by Edward Snowden reveal that both the British Intelligence and the NSA regularly intercept the British MPs emails.
According to Computer Weekly, new documents leaked by Edward Snowden reveal that both the British Intelligence and the NSA regularly intercept the British MPs emails and peers.
The revelations have been made public through an investigation by Computer Weekly, based on leaked documents by the now-exiled former NSA contractor Edward Snowden.
The GCHQ and the NSA intercepted sensitive emails of British MPs and the privileged correspondence between parliamentarians and their constituents, the surveillance leveraged on the Parliament’s Microsoft computer system, Office 365.
The British cyber spies alleged accessed the emails when they leave the UK in transit to Microsoft’s data centers in Dublin and the Netherlands
“GCHQ documents classified above top secret, released by NSA whistleblower Edward Snowden, also reveal that the spy agency has the capability to scan the content of parliamentary emails for “keywords” through an established cyber defence network that is connected to commercial software used to filter spam emails from MPs’ inboxes.” reported Computer Weekly.
At least since 2014, the GCHQ used its Tempora interception system to collect metadata related to the parliamentary emails, including sender, recipient and subject matter.
“The controversial decision by Parliament to replace its internal email and desktop office software with Microsoft’s Office 365 service in 2014, means that parliamentary data and documents constantly pass in and out of the UK to Microsoft’s datacentres in Dublin and the Netherlands, across the backbone of the internet.”
The Tempora system allowed the GCHQ to scan the content of parliamentary emails searching for specific keywords.
The NSA Prism program was used by the NSA to access all parliamentary documents and email through Microsoft Office 365 software, as a result of secret directives given to Microsoft under the US 2008 surveillance laws. The same directives were implemented by Microsoft that provided the cloud email system Office 365 to the British Houses of Parliament.

The MPs’ communications have been partially protected from interception under the “Wilson Doctrine,” introduced in 1968, but it doesn’t protect communications that leave the UK’s borders, this lack of protection is exploited by the GCHQ spies.
“The House of Commons administration has serious questions to answer,” Tory MP David Davis told Computer Weekly.
“On whose authority was ‘consent’ granted to view members’ emails? How did they manage to obtain that consent from every one of the 650 members whose constituents’ confidentiality is affected?” the former Home Office minister asked.
“The government should also make it clear to parliament the extent to which scanning of all mail by a US-controlled company has made Parliamentary communications vulnerable to agencies of a foreign power, namely the American NSA,” he added.
British MP defined as shocking these revelations that urge an action from the UK Government.
https://www.surveymonkey.com/r/secbloggerwards2016
Thank you
Pierluigi
[adrotate banner=”9″]
(Security Affairs – GCHQ, MPs emails)


