
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Geodo, the banking trojan with email self-spreading feature

Security researchers from Seculert firm have discovered a variant of the Cridex banking worm, dubbed Geodo, which spreads itself through email. In the last months a significant number of banking trojans have been proposed by cyber criminal ecosystem, from EMOTET to Dyreza, criminals have used a wide casuistry of techniques to deceive bank customers. The primary purpose of the […]

Geodo, the banking trojan with email self-spreading feature

Security researchers from Seculert firm have discovered a variant of the Cridex banking worm, dubbed Geodo, which spreads itself through email.

In the last months a significant number of banking trojans have been proposed by cyber criminal ecosystem, from EMOTET to Dyreza, criminals have used a wide casuistry of techniques to deceive bank customers.

The primary purpose of the malware authors is to spread the banking trojan infecting as many victims as possible, last malicious code detected by security experts at Seculert dubbed Geodo, a new version of the Cridex (aka Feodo or Bugat) banking Trojan, implements a feature to spread itself in an efficient way.
Cridex is a banking worm which uses as attack vector removable drives, a second malware dropped by other malware or the download of a file hosted on a compromised website.
Geodo target Windows machined and works in conjunction with a worm that use as attack vector the email, it is able to propagate the infection sending out emails automatically.
“Recent efforts by our Research Lab has revealed new activity related to Cridex. As you may recall, Cridex is a data stealer also referred to as Feodo, and Bugat. The new Cridex version we are seeing now, aka Geodo, combines a self-spreading infection method–effectively turning each bot in the botnet into a vehicle for infecting new targets.” has written Aviv Raff, CTO at Seculert, in a blog post.
Once Geodo has infected the victim, it drops an additional piece of malware from the C&C servers which includes approximately 50,000 stolen SMTP account credentials including those of the associated SMTP servers.
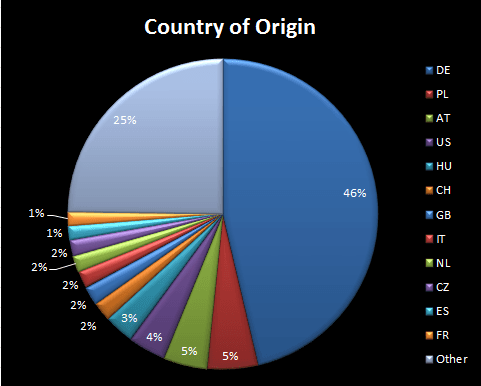
Geodo banking trojan
The stolen SMTP credentials used by Geodo allows the malware to send out emails from legitimate accounts, according to the data published by the security firm, the Germany is the country with the major number of infections followed by Austria, Hungary and the US.
Banking users infected by Geodo were targeted through a phishing attack, Phishing mails include a link to download a zip file containing the malware disguised as an invoice or Shipment PDF file.

“The C&C provides the malware with a batch of 20 targeted email addresses.The malware is also given a from address, subject line, and email body text unique to this particular batch of emails. Once the malware has run through the batch, it is provided with a new batch of 20 emails. And with each new batch of emails the C&C also sends a new from address, subject line, and body.”

geodo email

“The emails we have seen, written in German, contain a link prompting the recipient to download a zip file which contains an executable disguised as a PDF document,” “By opening the file, Geodo [new version of Cridex] is installed on the newly infected endpoint, adding a new bot to the mix.” states Seculert in the blog post.

geodo infection

Like many other banking malware, also Geodo is able to inject code into the browser to conduct operations in the name of the victims and manipulate content proposed through the browser to the bank customer.
Banking customers must be aware that cybercrime  is very prolific, knowing the threats could help to mitigate them.
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs –  Geodo,  banking trojan)

[adrotate banner=”5″]

[adrotate banner=”13″]


