
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hacker leaks info of pro-Trump GETTR members online

A hacker has leaked claims to have breached pro-Trump GETTR and leaked the private information of almost 90,000 members on a hacking forum. GETTR is a new pro-Trump social media platform created by Jason Miller, a former Trump advisor, the Twitter-like platform suffered a data breach. The security breach comes a few hours after its […]

GETTR

A hacker has leaked claims to have breached pro-Trump GETTR and leaked the private information of almost 90,000 members on a hacking forum.

GETTR is a new pro-Trump social media platform created by Jason Miller, a former Trump advisor, the Twitter-like platform suffered a data breach.

The security breach comes a few hours after its launch on July 4.

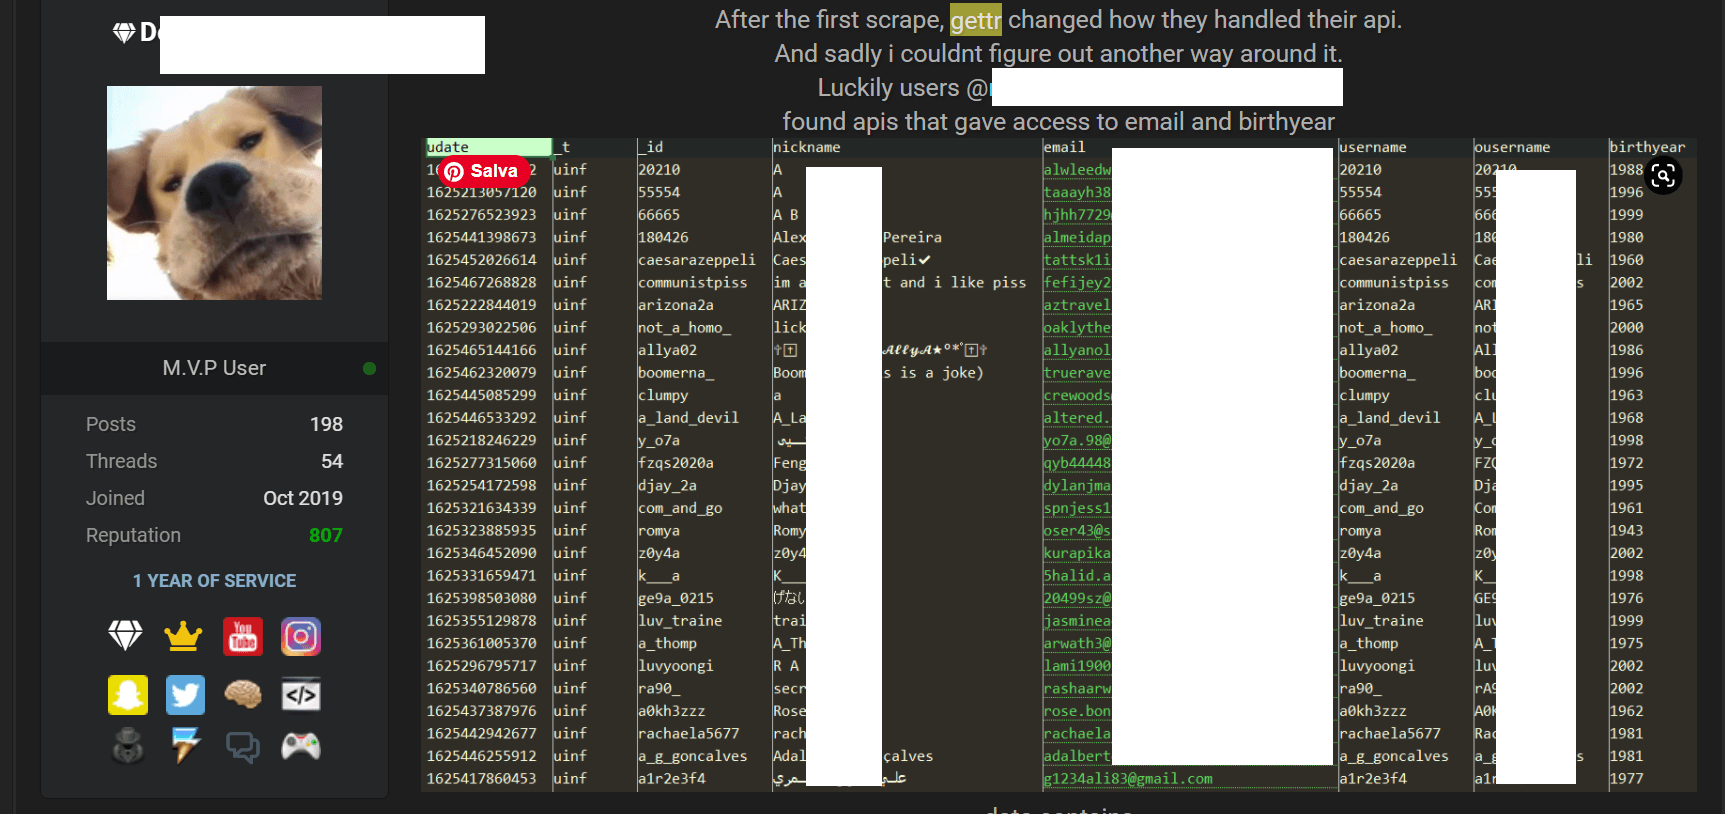
A threat actor claimed to have scraped the private information of almost 90,000 members by abusing an unsecured API and published it on the RAID hacking forum.

GETTR

The exposed data includes member’s email address, nickname, profile name, profile descriptions, birth year, location, personal website, avatar URL, background images, and other data.

The data published on the hacking forum belongs to two lots, which were respectively shared on July 1 and July 5.

The first set of data was the result of a scraping activity, while the second one was obtained by abusing the unsecured GETTR API.

Multiple websites confirmed the authenticity of the data.

“The leaked data was authentic, according to checks performed by The Record.” reported The Record.

The availability of such kind of information exposes members of the social network at risk of cyberattacks, such as phishing attempts and frauds.

Members of the social network should remain vigilant on any suspicious message pretending to be from GETTR.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)

[adrotate banner=”5″]

[adrotate banner=”13″]


