
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

NSA releases the source code of the GHIDRA reverse engineering framework

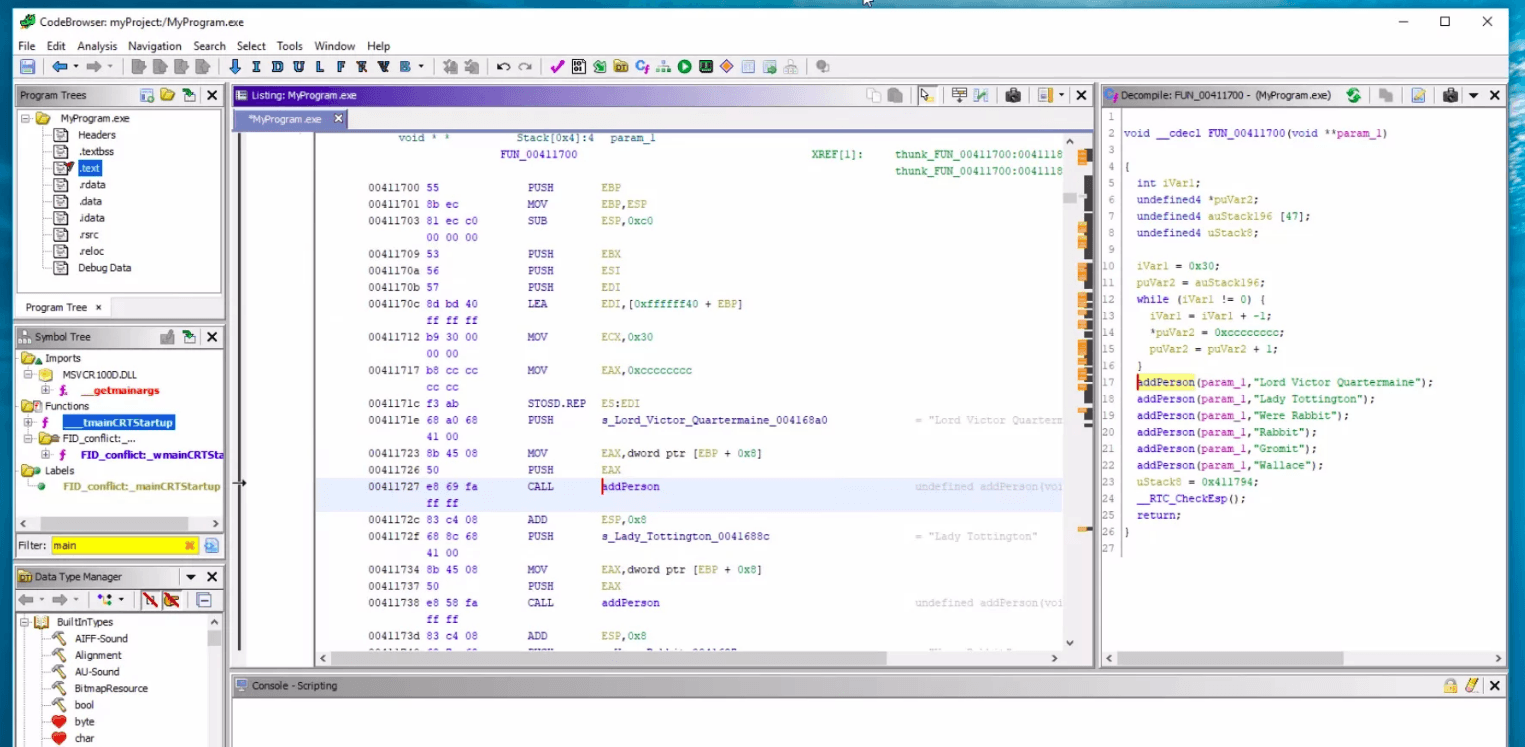
NSA released the complete source code for its GHIDRA suite, the version 9.0.2 is available on the Agency’s Github repository. In January 2019, the National Security Agency (NSA) announced the release at the RSA Conference of the free reverse engineering framework GHIDRA. GHIDRA is a multi-platform reverse engineering framework that runs on major OSs (Windows, […]

Ghidra

NSA released the complete source code for its GHIDRA suite, the version 9.0.2 is available on the Agency’s Github repository.

In January 2019, the National Security Agency (NSA) announced the release at the RSA Conference of the free reverse engineering framework GHIDRA.

GHIDRA is a multi-platform reverse engineering framework that runs on major OSs (Windows, macOS, and Linux).

The framework was first mentioned in the CIA Vault 7 dump that was leaked in 2017. WikiLeaks obtained thousands of files allegedly originating from a CIA high-security network that details CIA hacking techniques, tools, and capabilities. Digging in the huge trove of files, it is possible to find also information about the GHIDRA, a Java-based engineering tool.

Early March, the NSA has released the suite Ghidra that could be used to find vulnerabilities and security holes in applications.

Ghidra is Apache 2.0-licensed and requires a Java runtime, it is available
for download here. 

You can download the GHIDRA source code and its component from the following links:

The platform was presented at the RSA Conference in San Francisco on Tuesday by Rob Joyce, former head of the NSA’s elite hacking team and now White House cybersecurity coordinator,

Joyce has presented the code-analysis suite, he remarked the absence of backdoors.

“There is no backdoor in Ghidra,” he announced. “This is the last community you want to release something out to with a backdoor installed, to people who hunt for this stuff to tear apart.”

Ghidra

After the release of GHIDRA some security experts and malware researchers have demonstrated how to use it in practical analysis. My colleagues at Cybaze-Yoroi ZLAB malware demonstrated how to use the NSA Ghidra suite in a real case study, the analysis of the AZORult malware.

Enjoy it!

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Ghidra, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


