
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Godlua backdoor, the first malware that abuses the DNS over HTTPS (DoH)

Researchers at Network Security Research Lab of Qihoo 360 discovered a Lua-based backdoor dubbed Godlua that targets both Linux and Windows systems. The peculiarity of this new piece of malware is the ability to communicate with C2 servers via DNS over HTTPS (DoH). The DoH protocol was a new standard proposed in October 2018 and it is […]

Godlua Backdoor

Researchers at Network Security Research Lab of Qihoo 360 discovered a Lua-based backdoor dubbed Godlua that targets both Linux and Windows systems.

The peculiarity of this new piece of malware is the ability to communicate with C2 servers via DNS over HTTPS (DoH).

The DoH protocol was a new standard proposed in October 2018 and it is currently supported by several publicly available DNS servers. Some web browsers, including Google Chrome and Mozilla Firefox also support the DoH.

Godlua is a DDoS bot that was already involved in attacks in the wild, such as the one that hit liuxiaobei[.]com domain.

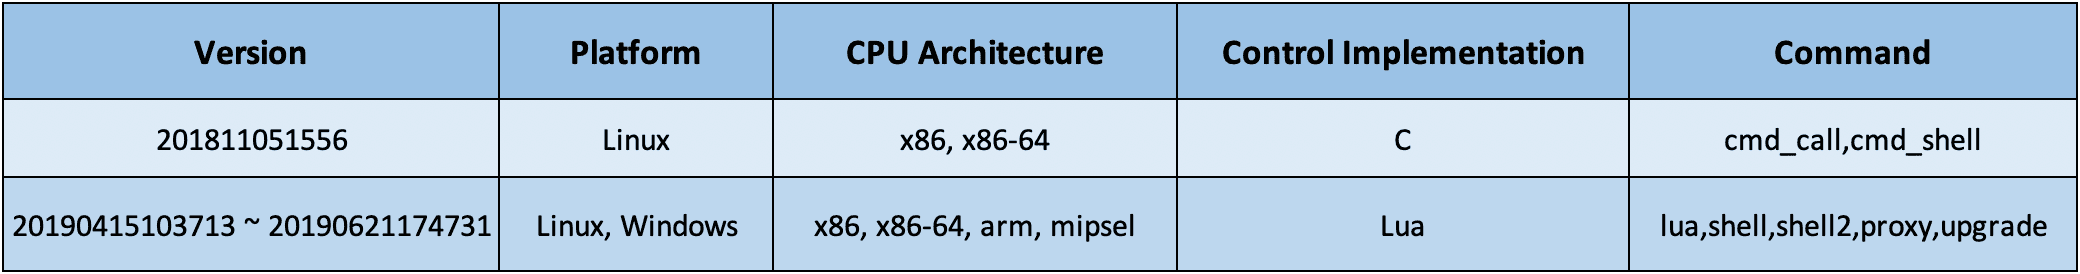
The experts analyzed two samples of the Godlua backdoor, one for Linux boxes (version 201811051556) and the other for Windows systems, the latter supporting more built-in commands and more CPU architectures (version 20190415103713 ~ 2019062117473)

Only the second sample, the Windows one, appears to be continuously updated.

The version developed to target the Linux boxes only supports two types of instructions, it could run custom files and execute Linux commands.

The second variant. version 20190415103713 ~ 20190621174731, is able to infect both Windows and Linux, its control module is implemented in Lua and supports five C2 commands.

“The Bot sample downloads many Lua scripts when executing, and the scripts can be broken down to three categories: execute, auxiliary, and attack.” reads the analysis published by the experts.

Godlua Backdoor

At the time of writing, experts at Qihoo 360 are investigating infection vectors, they discovered that some Linux machines were infected by exploiting the Confluence exploit for CVE-2019-3396.

Back to the use of DoH, the goal of the protocol is to increase user privacy and security by preventing eavesdropping and manipulation of DNS data.

The same protocol is used by the Godlua backdoor to hide the communications with the C2 servers.

“Godlua Backdoor has a redundant communication mechanism for C2 connection, a combination of hardcoded dns name, Pastebin.com, GitHub.com as well as DNS TXT are used to store the C2 address, which is not something we see often.” states the analysis. “At the same time, it uses HTTPS to download Lua byte-code files, and uses DNS over HTTPS to get the C2 name to ensure secure communication between the bots, the Web Server and the C2.”

Godlua is the first malware that abuses the DNS over HTTPS (DoH) protocol to protect its command and control infrastructure.

Additional details on the backdoor, including indicators of compromise (IOCs) are reported in the Qihoo 360’s analysis.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Godlua backdoor, DoH)

[adrotate banner=”5″]

[adrotate banner=”13″]


