
Security experts reported widespread Google Groups misconfiguration exposes sensitive information.
Administrators of organizations using Google Groups and G Suite must review their configuration to avoid the leakage of internal information.
Security researchers from Kenna Security have recently discovered that 31 percent of 9,600 organizations analyzed is leaking sensitive e-mail information.
The list of affected entities also includes Fortune 500 companies, hospitals, universities and colleges, newspapers and television stations, and even US government agencies.
“Organizations utilizing G Suite are provided access to the Google Groups product, a web forum directly integrated with an organization’s mailing lists. Administrators may configure a Google Groups interface when creating a mailing list.” reads the blog post published by Kenna Security.
“Due to complexity in terminology and organization-wide vs group-specific permissions, it’s possible for list administrators to inadvertently expose email list contents. In practice, this affects a significant number of organizations”
The discovery is not new, back in 2017 experts discovered wrong configurations of G Suite that can lead to data leakage.
Unfortunately, since the first advisory published by experts at RedLock, many installs continue to leak data. According to Kenna Security, the main reason is Google Groups uses a complex terminology and organisation-wide vs group-specific permissions.
“Due to complexity in terminology and organization-wide vs group-specific permissions, it’s possible for list administrators to inadvertently expose email list contents. In practice, this affects a significant number of organizations” continues the post.
When a G Suite admin creates a Groups mailing list for specific recipients, it configures a Web interface for the list, available to users at https://groups.google.com.
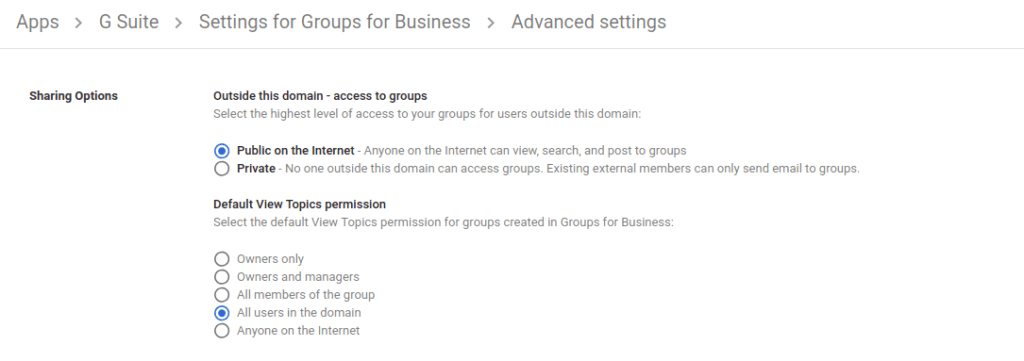
Google Group privacy settings for individuals can be adjusted on both a domain and a per-group basis. In affected organizations, the Groups visibility setting is available by searching “Groups Visibility” after logging into https://admin.google.com and it is configured to “Public on the Internet”

To discover if an organization is affected, administrators can browse to the configuration page by logging into G Suite as an administrator and typing “Settings for Groups for Business” or simply using this direct link.
“In almost all cases – unless you’re explicitly using the Google Groups web interface – this should be set to “Private”.” continues the post.
“If publicly accessible, you may access your organization’s public listing at the following link: https://groups.google.com/a/[DOMAIN]/forum/#!forumsearch/”
Administrators have to set as private the “Google Group” to protect internal information such as customer reviews, invoices payable, password recovery / reset e-mails, and more.
It is important to highlight that Google doesn’t consider configuration issues as a vulnerability, experts recommend administrators to read the Google Groups documentation, set the sharing setting for “Outside this domain – access to groups” to “private”.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – G Suite, Google Groups)
[adrotate banner=”5″]
[adrotate banner=”13″]


