
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Attackers can discover IP address by sending a link over the Skype mobile app

A security researcher demonstrated how to discover a target’s IP address by sending a link over the Skype mobile app. The security researcher Yossi discovered that is possible to discover a target’s IP address by sending a link over the Skype mobile app. The researcher pointed out that the attack only requires the target to […]

Attackers can discover IP address by sending a link over the Skype mobile app

A security researcher demonstrated how to discover a target’s IP address by sending a link over the Skype mobile app.

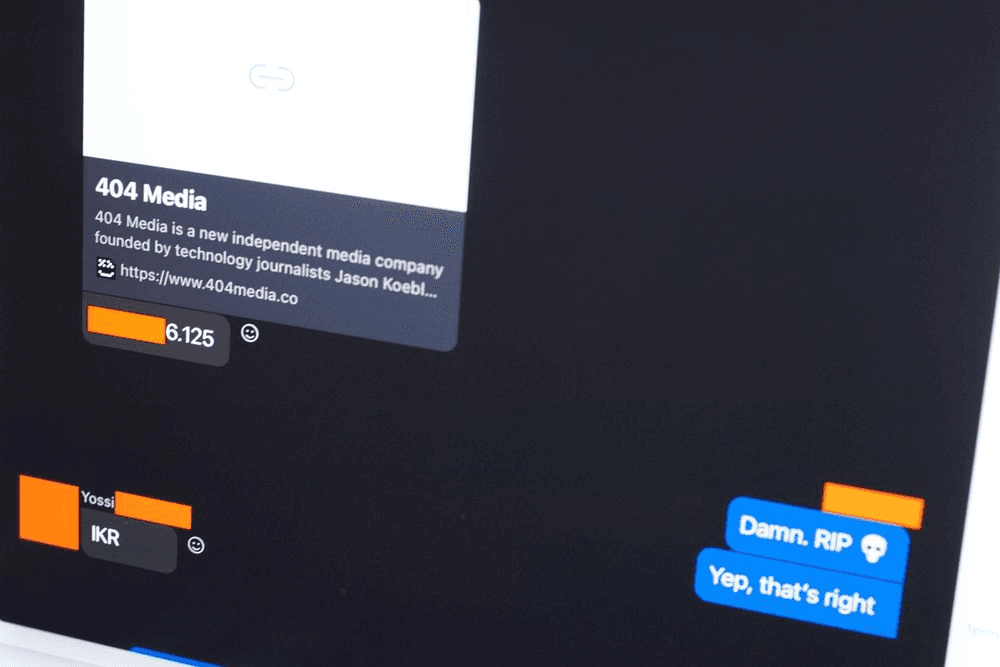
The security researcher Yossi discovered that is possible to discover a target’s IP address by sending a link over the Skype mobile app. The researcher pointed out that the attack only requires the target to open the message. The problem only impacts the Skype mobile app.

The knowledge of the IP address can allow threat actors to find the physical location of the target posing a risk to their privacy, security, and safety.

According to 404 Media, Yossi reported the issue to Microsoft earlier this month, but it seems that the company initially downplayed the problem and gave no indication that it plans to address the flaw.

“[the] disclosure of an IP address is not considered a security vulnerability on it’s [sic] own,” Microsoft told Yossi.

However, after 404 Media contacted Microsoft for comment, the IT giant announced it plans to fix the problem in an upcoming update.

“The attack could pose a serious risk to activists, political dissidents, journalists, those targeted by cybercriminals, and many more people.” state 404 Media “At minimum, an IP address can show what area of a city someone is in. An IP address can be even more revealing in a less densely populated area, because there are fewer people who could be associated with it.”

The popular cybersecurity reporter JOSEPH COX, personally tested Yossi’s attack.

Cox explained that the technique was working both when he connected to Skype using a virtual private network and when he connected to a public Wi-Fi network without a VPN.

Source 404media

404 Media only revealed that the issue is simply exploitable by manipulating a certain parameter related to the link. The reporters did not share details of the attacks because the flaw has yet to be fixed.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Skype)


