
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Grief ransomware gang hit US National Rifle Association (NRA)

Grief ransomware operators claim to have compromised computer systems at US National Rifle Association (NRA) and added it to their leak site. Grief ransomware operators announced to have hacked US National Rifle Association (NRA) and threaten to leak the stolen data. The NRA was added to the list of compromised organizations on the leak site […]

NRA

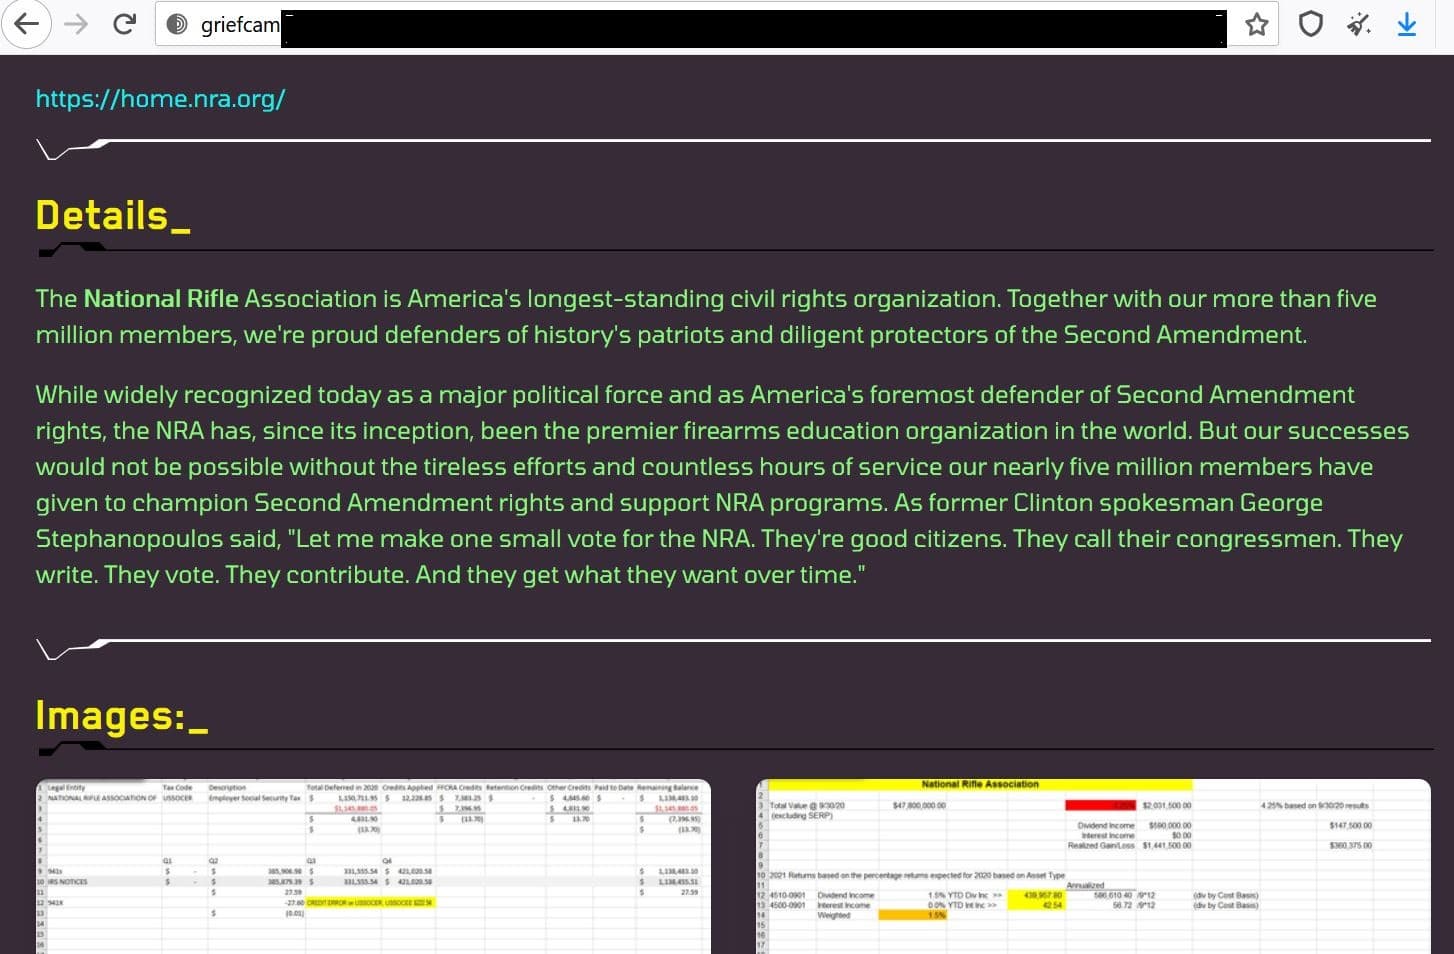
Grief ransomware operators claim to have compromised computer systems at US National Rifle Association (NRA) and added it to their leak site.

Grief ransomware operators announced to have hacked US National Rifle Association (NRA) and threaten to leak the stolen data.

The NRA was added to the list of compromised organizations on the leak site of the group, that gang also published a set of documents as proof of the hack. The analysis of the sample doesn’t allow to determine whether the gang breached the organization or one of its branches.

NRA

Researchers link the Grief ransomware to the DoppelPaymer operations that is considered part of the Evil Corp.

Evil Corp has recently launched a new ransomware called Macaw Locker to evade US sanctions that prevent victims from making ransom payments.

The Evil Corp cybercrime group (aka the Dridex gang Indrik Spider, the Dridex gang, and TA505) has been active in cybercrime activities since 2007. The group started its operations by developing and distributing the infamous Dridex banking Trojan, then it switched to ransomware operation by infecting victims’ computer networks with the BitPaymer ransomware.

In 2019, the U.S. Department of Justice (DoJ) has charged Russian citizens Maksim V. (32) and Igor Turashev (38) for distributing the infamous Dridex banking Trojan, and for their involvement in international bank fraud and computer hacking schemes.

The US Government announced sanctions for ransomware negotiation firms that will support victims of the Evil Corp group in the ransom payments.

Due to these sanctions, Evil Corp launched several ransomware operations that employed different strains of ransomware, such as WastedLocker, Hades, Phoenix Locker, and PayloadBin.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, NRA)

[adrotate banner=”5″]

[adrotate banner=”13″]


