
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Group Health Cooperative data breach impacted 530,000 individuals

Group Health Cooperative of South Central Wisconsin disclosed a data breach that impacted over 500,000 individuals. The Group Health Cooperative of South Central Wisconsin (GHC-SCW) is a non-profit organization that provides health insurance and medical care services to its members in the Madison metropolitan area of Wisconsin. The organization disclosed a data breach after a […]

Group Health Cooperative

Group Health Cooperative of South Central Wisconsin disclosed a data breach that impacted over 500,000 individuals.

The Group Health Cooperative of South Central Wisconsin (GHC-SCW) is a non-profit organization that provides health insurance and medical care services to its members in the Madison metropolitan area of Wisconsin.

The organization disclosed a data breach after a ransomware attack, the incident impacted 533,809 individuals.

The data breach occurred on January 24, 2024, and was discovered on January 25 when GHC-SCW identified unauthorized access to its network. The Information Technology (IT) Department isolated and secured the organization’s network in response to the incident.

The Group Health Cooperative of South Central Wisconsin (GHC-SCW) notified the FBI and is responding to the incident with the help of external cybersecurity experts.

“The attacker attempted to encrypt GHC-SCW’s system but was unsuccessful.” reads the data breach notification shared with the Maine Attorney General. “On February 9, 2024, during our investigation, we discovered indications that the attacker had copied some of GHC-SCW’s data, which included protected health information (PHI).”

The potentially compromised PHI may have included member/patient name, address, telephone number, e-mail address, date of birth and/or death, social security number, member number, and Medicare and/or Medicaid number.

A ransomware group contacted the organization claiming the theft of data.

“Our discovery was confirmed when the attacker, a foreign ransomware gang, contacted GHC-SCW claiming responsibility for the attack and stealing our data,” continues the notification letter.

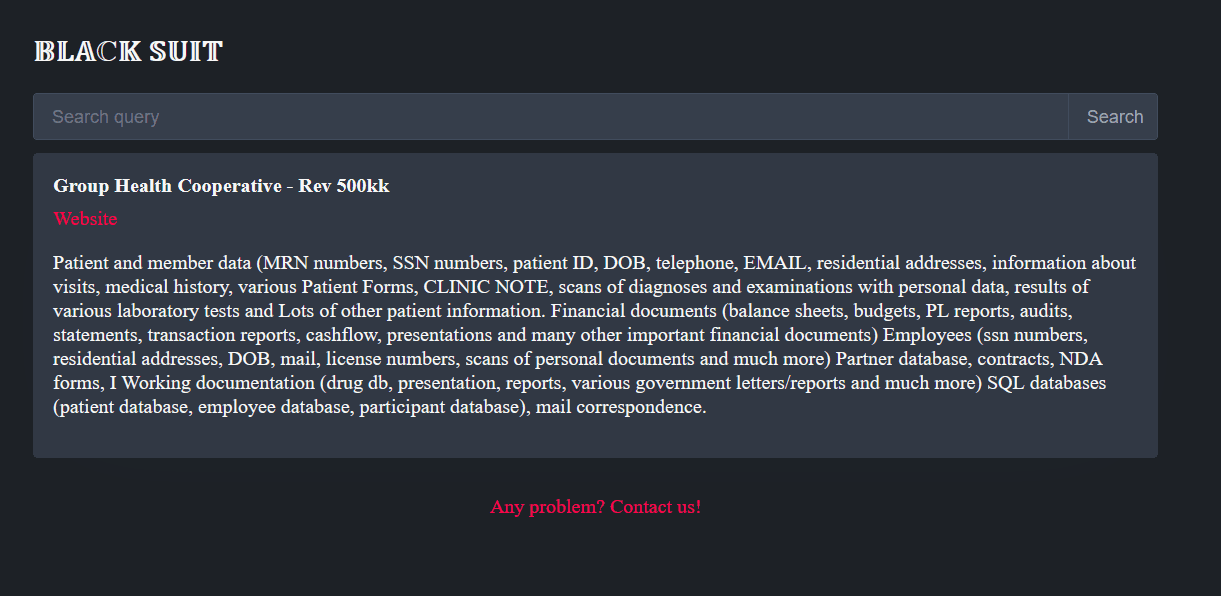
The data breach notification doesn’t name the ransomware group that hit the organization, however the BlackSuit gang added Group Health Cooperative to it Tor leak site in March. The ransomware group claimed to have stolen patient and member data, financial documents, employee data, NDAs, contracts, several databases, and emails.

Group Health Cooperative

The company pointed out that they have no indication that information has been used or further disclosed.

Group Health Cooperative also added that they have implemented enhanced security measures across all our systems and networks.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Group Health Cooperative)


