
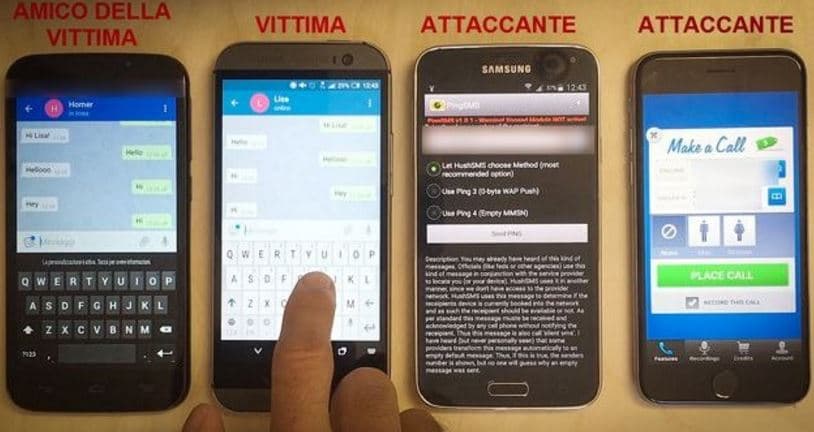
Researchers at InTheCyber firm have discovered a new easy exploitable and dangerous vulnerability affecting messaging systems.
InTheCyber – Intelligence & Defense Advisors (www.inthecyber.com), a leader in offensive & Defensive Cyber Security, has discovered in its R&D Labs a new easy and dangerous vulnerability affecting messaging systems.
Voicemail caller-id spoofing it’s a quite old flaw. When the mobile operator relies on caller-id to authenticate the user inside his voicemail, an attacker could falsify his caller-id in order to impersonate the user and gain access to his voicemail. At the moment, two of the biggest Italy mobile operators allow this kind of attack.
This undoubtedly raises problems about the privacy of the communications, especially the information stored inside the voicemail. Moreover, this old flaw could be weaponized in order to compromise other services.
For example, Telegram, WhatsApp, and Signal, when an activation code is requested, as start forward an SMS with the activation code. If the code is not entered promptly, these services resend the activation code through an automated call.
Depending on the configuration of the voicemail of the user, the authentication code will be inside his voicemail in the following scenarios: user does not respond, the user is not reachable, the user is occupied. In the first scenario, an attacker could try to ask an activation code using the victim account during the night-time. In the second scenario, an attacker could send multiple Silent-SMS to the user in order to determine when the phone is detached from the network and start the attack. In the third, a telephone scam could be used during the attack to keep the phone busy.
In the first scenario, an attacker could try to ask an activation code using the victim account during the night-time. In the second scenario, an attacker could send multiple Silent-SMS to the user in order to determine when the phone is detached from the network and start the attack. In the third, a telephone scam could be used during the attack to keep the phone busy.
In the second scenario, an attacker could send multiple Silent-SMS to the user in order to determine when the phone is detached from the network and start the attack. In the third, a telephone scam could be used during the attack to keep the phone busy.

Besides caller-id spoofing often voicemail services rely on default or a guessable pin to authenticate a user, for example, when he tries to access his voicemail from another phone number.
Basically, if the voicemail is somehow accessible by an unauthorized person, and if no two-actor authentication is enabled, every service that relies on an automated call to send an activation code is hijackable.
Below a video PoC of the hack
 About the author: Paolo Lezzi
Founder & CEO at InTheCyber – Intelligence & Defense Advisors
[adrotate banner=”9″]
(Security Affairs – messaging systems, hacking)


