
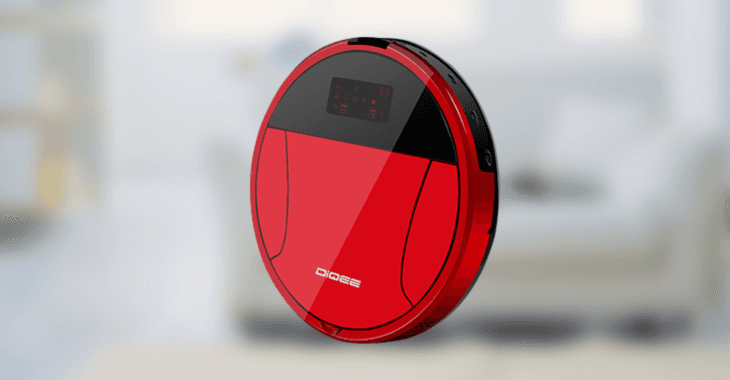
Positive Technologies discovered two flaws affecting Dongguan Diqee 360 smart vacuums that can be used to perform video surveillance.
Security researchers from Positive Technologies have discovered two vulnerabilities affecting Dongguan Diqee 360 smart vacuum cleaners that could be exploited by an attacker to run malicious code on a device with superuser privileges.
The flaws likely affect smart vacuum cleaners made by the company and sold under other brands as well, experts believe the issue could affect also other Dongguan devices, including DVRs, surveillance cameras, and smart doorbells.
“Like any other IoT device, these robot vacuum cleaners could be marshalled into a botnet for DDoS attacks, but that’s not even the worst-case scenario, at least for owners. Since the vacuum has Wi-Fi, a webcam with night vision, and smartphone-controlled navigation, an attacker could secretly spy on the owner” reads the post published by Positive Technologies.
The two vulnerabilities have been tracked as CVE-2018-10987 and CVE-2018-10988, the former could be exploited by a remote attacker meanwhile the latter needs physical access to the device.
The first bug can only be exploited by an authenticated attacker, but Positive Technologies says all Diqee 360 devices come with a default password of 888888 for the admin account, which very few users change, and which attackers can incorporate into their exploit chain.

” An attacker can discover the vacuum on the network by obtaining its MAC address and send a UDP request, which, if crafted in a specific way, results in execution of a command with superuser rights on the vacuum.” reads the report published by the experts.
“The vulnerability resides in the REQUEST_SET_WIFIPASSWD function (UDP command 153). To succeed, the attacker must authenticate on the device—which is made easier by the fact that many affected devices have the default username and password combination (admin:888888).”
The second vulnerability requires physical access to be triggered, it can be exploited by an attacker to load a tainted version of the firmware by inserting a microSD card into the vacuum.
“A microSD card could be used to exploit weaknesses in the vacuum’s update mechanism. After the card is inserted, the vacuum update system runs firmware files from the upgrade_360 folder with superuser rights, without any digital signature check. Therefore, a hacker could create a special script, place it on a microSD card in the upgrade_360 folder, insert this card, and restart the vacuum. This script could run arbitrary code, such as a sniffer to intercept private data sent over Wi-Fi by other devices.” states the post.
Positive Technologies responsibly reported the flaws in the smart vacuums to the company giving it the time to address the vulnerabilities, unfortunately, it does not have any information about whether or not the vulnerabilities have been fixed to date
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Smart vacuums, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


