
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hacking Team Another Flash Zero-Day: CVE-2015-5122

Following the Hacking Team data breach, yet another Adobe Flash Player zero-day vulnerability has been found actively exploited in-the-wild. Another Flash Zero-Day: CVE-2015-5122 Yet another Adobe Flash Player zero-day has been found actively exploited in-the-wild. Thanks to the breach of the HackingTeam’s private files, another Adobe Flash zero-day has been made publicly accessible and hackers […]

Hacking Team Another Flash Zero-Day: CVE-2015-5122

Following the Hacking Team data breach, yet another Adobe Flash Player zero-day vulnerability has been found actively exploited in-the-wild.

Another Flash Zero-Day: CVE-2015-5122

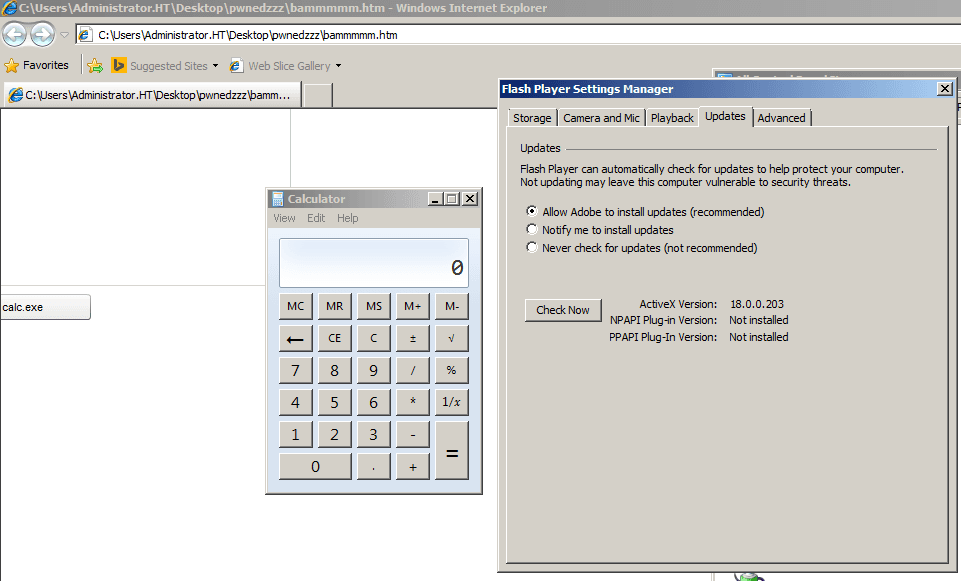
Yet another Adobe Flash Player zero-day has been found actively exploited in-the-wild. Thanks to the breach of the HackingTeam’s private files, another Adobe Flash zero-day has been made publicly accessible and hackers are taking full advantage.

Adobe gives credits to Dhanesh Kizhakkinan of FireEye for reporting CVE-2015-5122 and Peter Pi of TrendMicro for reporting CVE-2015-5123 and for working with Adobe to help protect our customers.
This new zero-day affects Adobe Flash Player up to version 18.0.0.203

hacking team zero-day exploit
Exploit Kits Leveraging this New Flash Zero-Day, Metasploit Module Created
A Metasploit Module has already been created that exploits this zero-day vulnerability. Additionally, this exploit has already been integrated into some popular exploit kits.
Currently, the following Exploit Kits have been found exploiting the Flash Player zero-day, now dubbed CVE-2015-5122:

  • Angler EK

Adobe expects to patch this vulnerability at some point during this coming week.

Special Thanks
Special thanks to Kafeine of Malware don’t need Coffee for his swift analyses and sharing of his findings, as always.
The source code of this exploit has been posted; the URL to download the source (within a compressed archive) was posted on Pastebin, and can be found by clicking here.

About the Author Michael Fratello

Michael Fratello is a Security Engineer employed by CipherTechs, Inc., a privately held information security services provider located in downtown Manhattan, New York.  Specializing in Penetration Testing and Digital Forensics, Michael, a St. John’s University graduate majoring in Computer Security Systems, has developed a passion for information security and often spends his free time studying, programming, and researching the exponentially growing number of threats found in-the-wild today.

Edited by Pierluigi Paganini

(Security Affairs –  Hacking Team, zero-day)


