
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Bogus News mobile App discovered in Hacking Team arsenal

Experts at Trend Micro have discovered a malicious Android App while they were analyzing the package of data stolen from Hacking Team. Experts at Trendmicro analyzing package of data stolen from Hacking Team systems discovered a fake news app that was designed to circumvent filtering in Google Play. The malicious app was downloaded only 50 […]

Bogus News mobile App discovered in Hacking Team arsenal

Experts at Trend Micro have discovered a malicious Android App while they were analyzing the package of data stolen from Hacking Team.

Experts at Trendmicro analyzing package of data stolen from Hacking Team systems discovered a fake news app that was designed to circumvent filtering in Google Play. The malicious app was downloaded only 50 times before being removed from Google Play on July 7.

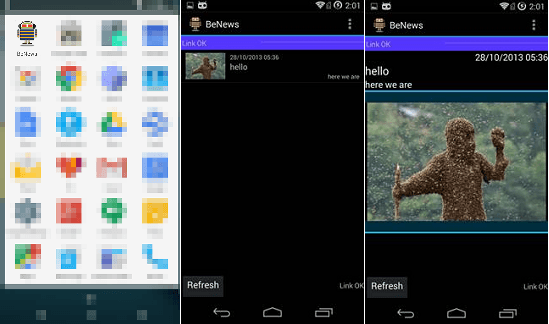
The app was called “BeNews” and is a backdoor app, that takes advantage of the extinct site “Benews”

“We found the backdoor’s source code in the leak, including a document that teaches customers how to use it. Based on these, we believe that the Hacking Team provided the app to customers to be used as a lure to download RCS Android malware on a target’s Android device.” States the blog post published by TrendMicro.

The backdoor included in the app is called “ANDROIDOS_HTBENEWS.A” and affects android devices from version 2.2 Froyo to 4.4.4 KitKat. The backdoor exploits the CVE-2014-3153 vulnerability, which is a local privilege escalation flaw.

“Looking into the app’s routines, we believe the app can circumvent Google Play restrictions by using dynamic loading technology. Initially, it only asks for three permissions and can be deemed safe by Google’s security standards as there are no exploit codes to be found in the app. However, dynamic loading technology allows the app to download and execute a partial of code from the Internet. It will not load the code while Google is verifying the app but will later push the code once the victim starts using it.” Continues the post.

The leaked dump also includes detailed instructions on how the Hacking Team’s clients could manipulate the backdoor:
Hacking Team mobile app 2

As usual, the scaring aspect of the story is that many other companies like the Hacking Team with similar abilities are using similar techniques to hack computing systems and mobile devices worldwide. Always pay attention on what you install in your device and use an endpoint product to protect it.

About the Author Elsio Pinto

Elsio Pinto is at the moment the Lead Mcafee Security Engineer at Swiss Re, but he also as knowledge in the areas of malware research, forensics, ethical hacking. He had previous experiences in major institutions being the European Parliament one of them. He is a security enthusiast and tries his best to pass his knowledge. He also owns his own blog http://high54security.blogspot.com/

Pierluigi Paganini

(Security Affairs – Hacking Team, Android)


