Avast released a free decryptor for variants of the Hades ransomware tracked as ‘MafiaWare666’, ‘Jcrypt’, ‘RIP Lmao’, and ‘BrutusptCrypt,’ .
Avast has released a decryptor for variants of the Hades ransomware known as ‘MafiaWare666’, ‘Jcrypt’, ‘RIP Lmao’, and ‘BrutusptCrypt,’ which can allow the victims of these ransomware strains to recover their files without paying the ransom.
The security firm discovered a bug in the encryption process implemented by the Hades ransomware that can be used to recover the files encrypted by some variants.
“We discovered a vulnerability in the encryption schema that allows some of the variants to be decrypted without paying the ransom. New or previously unknown samples may encrypt files differently, so they may not be decryptable without further analysis.” reads the post published by AVAST.
The experts pointed out that the Hades ransomware affected by the flaw did not exfiltrate any data from the victims. MafiaWare666, for example, is a ransomware strain written in C# which doesn’t contain any obfuscation or anti-analysis techniques. The malicious code encrypts files using AES encryption.
The malware samples analyzed by the researchers append the following extensions the the filename of the encrypted files:
- .MafiaWare666
- .jcrypt
- .brutusptCrypt
- .bmcrypt
- .cyberone
- .l33ch
Once the MafiaWare666 variant completes the encrypted process, it displays a window that provides payment instructions to the victims. The ransom price ranges from $50 to $300, although some of the older samples with different names demand up to one Bitcoin.
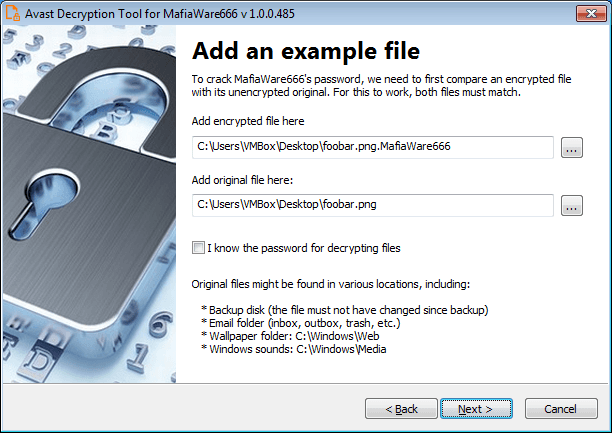
Victims of these variants can download the free decryptor from the Avast server along with instructions to use it.

The tool also allows victims that know a valid password for decrypting files, but that are not able to use the decryptor supplied by Hades, to tick the box in the above UI provided by the tool.
In case victims haven’t the password, they can use the Avast tool to crack it.
“Once the password is found, you can proceed to decrypt all the encrypted files on your PC by clicking “Next” concludes AVAST. ” On the final page, you can opt-in to backup your encrypted files. These backups may help if anything goes wrong during the decryption process. This option is on by default, which we recommend. After clicking “Decrypt” the decryption process begins. Let the decryptor work and wait until it finishes decrypting all of your files.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Hades ransomware)
[adrotate banner=”5″]
[adrotate banner=”13″]