
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Discovered a database containing data of 3.3 million Hello Kitty fans

The researcher Chris Vickery has discovered a database leak that exposed 3.3 million accounts belonging to Hello Kitty fans. The database of the official online community for Hello Kitty and other Sanrio characters, the sanriotown.com, has suffered a data breach. The researcher Chris Vickery has discovered online a database exposing 3.3 million accounts belonging to […]

Discovered a database containing data of 3.3 million Hello Kitty fans

The researcher Chris Vickery has discovered a database leak that exposed 3.3 million accounts belonging to Hello Kitty fans.

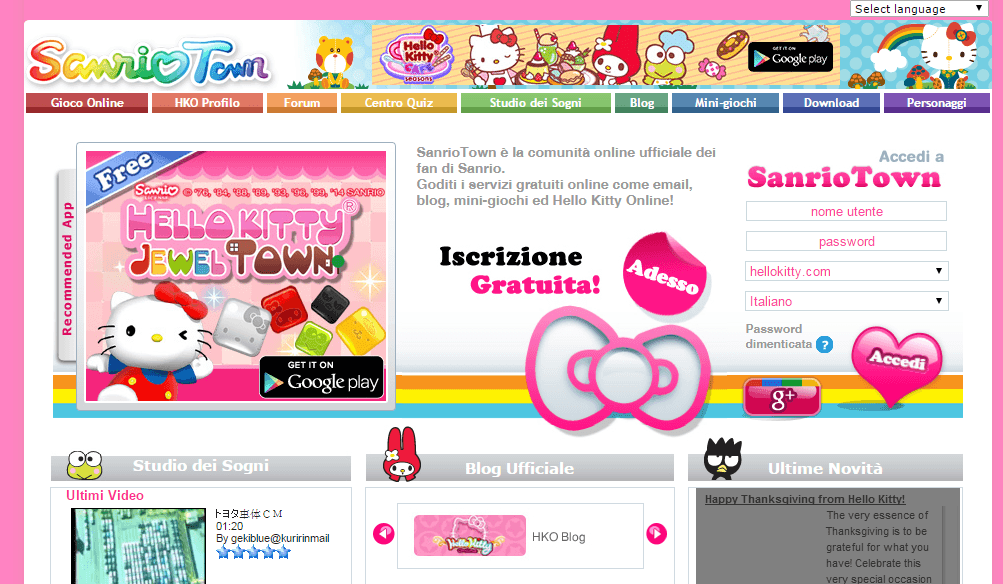
The database of the official online community for Hello Kitty and other Sanrio characters, the sanriotown.com, has suffered a data breach. The researcher Chris Vickery has discovered online a database exposing 3.3 million accounts belonging to Hello Kitty fans.

According to Vickery not only the primary database sanriotown.com was affected, the fan portals of the following websites were also impacted by the leak:

  • hellokitty.com;
  • hellokitty.com.sg;
  • hellokitty.com.my;
  • hellokitty.in.th;
  • mymelody.com.

On Saturday evening, Vickery reported the discovery to Databreaches.net and Salted Hash.

The records exposed include first and last names, gender, encoded birthday (easily reversible), country, email addresses, SHA-1 hash passwords, password hint questions with corresponding answers, and other information.

Hello Kitty portal

The expert also discovered two additional backup servers containing mirrored data, then he notified the data leak to both Sanrio and the ISP being used to host the database.

This incident is raising great concern in the IT security industry because one again personal information of children are exposed online.

At the end of November, the VTech toy maker has been hacked exposing data of 11.6 million people, 6.4 million of them belonging to children.

The recent VTech data breach exposed 11.6 million people, and 6.4 million of them were children.

The identity theft of a child is even more insidious because crooks could abuse of the stolen data for years.

Every time I receive news of a data breach I suggest affected users to the change password for all the websites that share the same login credentials.

The same suggestion is valid for users that share the same hint question and answer across different websites.

Pierluigi Paganini

(Security Affairs – Hello Kitty, data breach)


