
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Analyzing the Telegram-based Android remote access trojan HeroRAT

Researchers at CSE Cybsec ZLab analyzed shared published their analysis of the Telegram-based Android RAT tracked as HeroRAT. In June, researchers from security firm ESET discovered a new family of Android Remote Administration Tool (RAT), dubbed HeroRAT, that leverages the Telegram BOT API to communicate with the attacker. The use of Telegram API can be considered […]

HeroRAT

Researchers at CSE Cybsec ZLab analyzed shared published their analysis of the Telegram-based Android RAT tracked as HeroRAT.

In June, researchers from security firm ESET discovered a new family of Android Remote Administration Tool (RAT), dubbed HeroRAT, that leverages the Telegram BOT API to communicate with the attacker.

The use of Telegram API can be considered a new trend in Android RAT landscape, because other RAT families implementing the same functionalities, such as TeleRAT and IRRAT, were discovered in the wild before HeroRAT.

HeroRAT appeared very active in Iran where it was spreading through third-party app stores, through tainted social media and messaging apps.

ESET experts speculate that the HeroRAT borrows the source code of a malware appeared in the hacking community in March 2018, however, it has some characteristics that distinguish it different from IRRAT and TeleRAT. One of these features is the usage of the Xamarin Framework and TeleSharp Library for the development of the RAT.

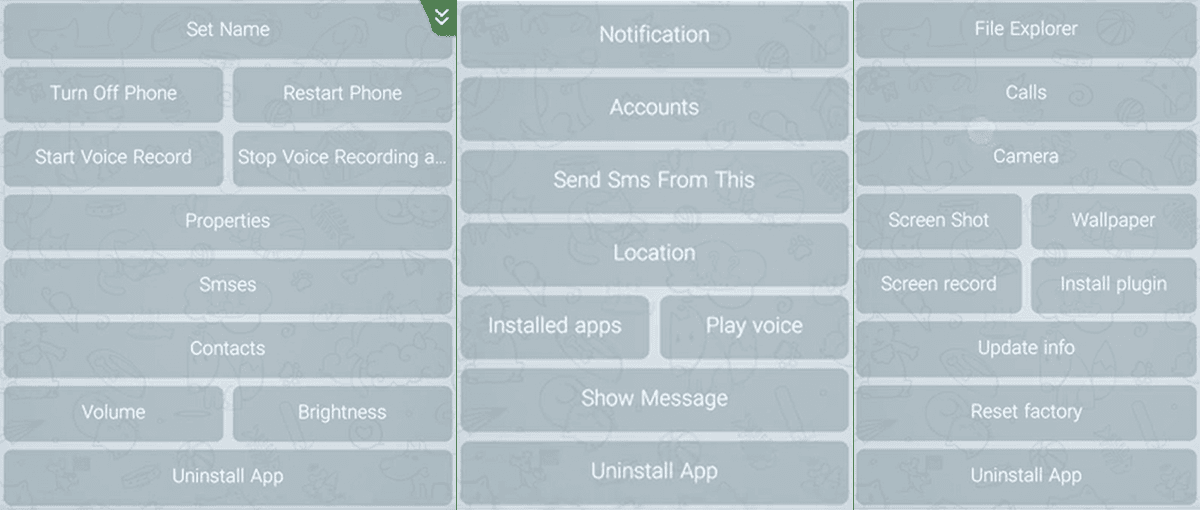
HeroRAT is offered for sale on a dedicated Telegram channel, the author offers three different variants depending on its functionalities: bronze (25 USD), silver (50 USD) and gold panels (100 USD). The malware author also released a demo video in which explains the RAT functionalities; below we have a screenshot from this demo video, showing the differences between the three variants.

Figure 1 – Differences between the RAT variants

Further details on the RAT analyzed by CSE Cybsec, including the IoCs and Yara Rules are available in the report published by researchers at ZLAb.

You can download the full ZLAB Malware Analysis Report at the following URL:

http://csecybsec.com/download/zlab/20180802_CSE_HeroRAT.pdf


[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – RAT, Telegram)

[adrotate banner=”5″]

[adrotate banner=”13″]


