Experts found vulnerabilities in HID Mercury Access Controllers can be exploited by attackers to remotely unlock doors.
Researchers from security firm Trellix discovered some critical vulnerabilities in HID Mercury Access Controllers that can be exploited by attackers to remotely unlock doors.
The flaws impact products manufactured by LenelS2, a provider of advanced physical security solutions (i.e. access control, video surveillance and mobile credentialing) owned by HVAC giant Carrier.
The vulnerabilities were disclosed during the Hardwear.io Security Trainings and Conference by researchers from Trellix Threat Labs who analyzed an industrial control system (ICS) used to grant physical access to privileged facilities. The experts focused on Carrier’s LenelS2 access control panels, manufactured by HID Mercury.
“Analysis begins at the lowest level of hardware. By using the manufacturer’s built-in ports, we were able to manipulate on-board components and interact with the device.Combining both known and novel techniques, we were able to achieve root access to the device’s operating system and pull its firmware for emulation and vulnerability discovery.” reads the post published by Trellix.
Trellix discovered eight vulnerabilities, seven of which have been rated as “critical,” which can be exploited by a remote attacker to execute arbitrary code, to perform command injection, information spoofing, write arbitrary files, and trigger a denial-of-service (DoS) condition. Below is the list of flaws discovered by the researchers:
| CVE | Detail Summary | Mercury Firmware Version | CVSS Score |
| CVE-2022-31479 | Unauthenticated command injection | <=1.291 | Base 9.0, Overall 8.1 |
| CVE-2022-31480 | Unauthenticated denial-of-service | <=1.291 | Base 7.5, Overall 6.7 |
| CVE-2022-31481 | Unauthenticated remote code execution | <=1.291 | Base 10.0, Overall 9.0 |
| CVE-2022-31486 | Authenticated command injection | <=1.291 (no patch) | Base 8.8, Overall 8.2 |
| CVE-2022-31482 | Unauthenticated denial-of-service | <=1.265 | Base 7.5, Overall 6.7 |
| CVE-2022-31483 | Authenticated arbitrary file write | <=1.265 | Base 9.1, Overall 8.2 |
| CVE-2022-31484 | Unauthenticated user modification | <=1.265 | Base 7.5, Overall 6.7 |
| CVE-2022-31485 | Unauthenticated information spoofing | <=1.265 | Base 5.3, Overall 4.8 |
Most of these vulnerabilities can be exploited without authentication, but exploitation requires a direct connection to the targeted system.
The researchers performed a reverse engineering of the firmware and system binaries, along with live debugging, and discovered the eight issues, six of them are unauthenticated and two authenticated vulnerabilities exploitable remotely over the network.
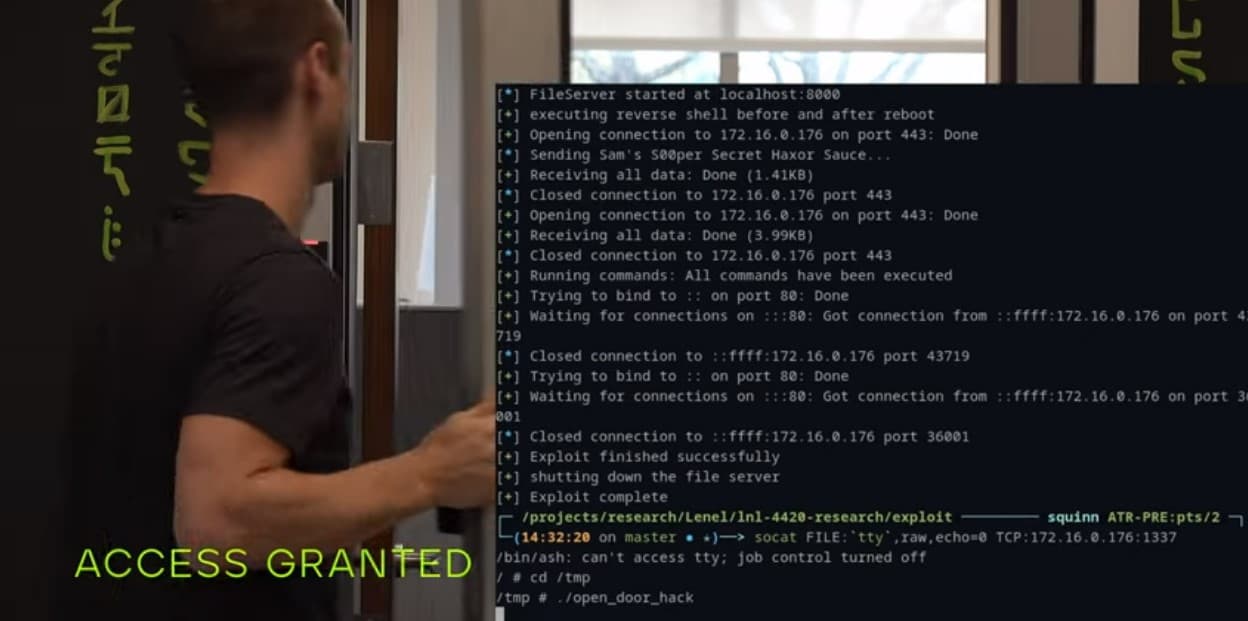
“By chaining just two of the vulnerabilities together, we were able to exploit the access control board and gain root level privileges on the device remotely. With this level of access, we created a program that would run alongside of the legitimate software and control the doors.” continues the post. “This allowed us to unlock any door and subvert any system monitoring.”
The experts also developed a proof-of-concept (PoC) exploit to unlock any door and hack monitoring systems. Below the video PoC published by the researchers:

Carrier has published a product security advisory to warn customers about the vulnerabilities and urge them to install firmware updates.
“By use of our responsible disclosure procedures independent penetration testing of HID Mercury™, access panels sold by LenelS2 were reported to contain cybersecurity vulnerabilities.” reads the advisory. “These vulnerabilities could lead to disruption of normal panel operations. The impacted LenelS2 part numbers include:
- LNL-X2210
- S2-LP-1501
- LNL-X2220
- S2-LP-1502
- LNL-X3300
- S2-LP-2500
- LNL-X4420
- S2-LP-4502
- LNL-4420
Prior generations of HID Mercury controllers are not impacted.
The US Cybersecurity and Infrastructure Security Agency (CISA) has also published an advisory about these vulnerabilities.
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, HID Mercury Access Controllers)
[adrotate banner=”5″]
[adrotate banner=”13″]