
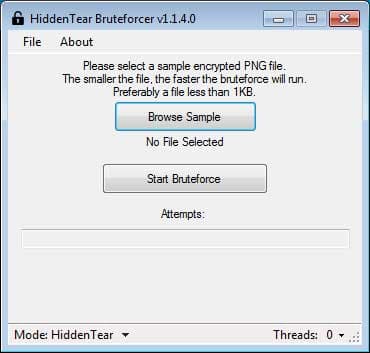
Good news for the victims of the dreaded HiddenTear Ransomware, the popular cybersecurity expert Michael Gillespie has devised a tool dubbed HT Brute Forcer that could allow decrypting files for free.
In 2015, the Turkish security researchers Utku Sen published the HiddenTear ransomware, the first open source ransomware, for educational purposes.
The original code was decryptable, for this reason, many other variants based on it were decryptable too.
HT Brute Forcer currently supports several HiddenTear variants, including:
8lock8, AnonCrack, Assembly, Balbaz, BankAccountSummary, Bansomqare Wanna, Blank, BloodJaws, Boris, CerberTear, CryptConsole2, CryptoKill, CyberResearcher, Data_Locker, Dev-Nightmare 2xx9, Diamond, Domino, Donut, dotRansom, Executioner, Executioner2, Executioner3, Explerer, FlatChestWare, Frog, Fuck_You, Gendarmerie, Horros, JobCrypter, Jodis, J-Ransomware, J-Want-To-Cry, Karmen, Kraken 2.0, Kratos, LanRan, Lime, Lime-HT, Luv, Matroska, MireWare, MoonCrypter, MTC, Nobug, Nulltica, onion3cry, OpsVenezuela, Paul, PayOrDie, Pedo, PGPSnippet, Poolezoor, Pransomware, Predator, Qwerty, Random6, Random6 2, Randion, RansomMine, Rootabx, Saramat, Shrug, ShutUpAndDance, Sorry, Symbiom, TearDr0p, Technicy, The Brotherhood, TheZone, tlar, TotalWipeOut, TQV, Ton, VideoBelle, WhiteRose, WhiteRose2, Zalupaid, ZenCrypt, Zenis, ZeroRansom, ZorroVictims of the HiddenTear Ransomware could follow the step by step procedure, published by Bleeping Computer, to decrypt their files for free.
- Download the HT Brute Forcer.
- Extract the downloaded hidden-tear-bruteforcer.zip and execute the HiddenTear Bruteforcer.exe.

- Click on the Browse Sample button and choose an encrypted PNG file. Experts suggest choosing the smaller one.
- Click on the Start Bruteforce button to start brute forcing the decryption key. The process can take some time.
- When the tool has found the encryption key, the decryptor will automatically decrypt the
test file and ask the users to determine if it was correctly decrypted. - If the file was decrypted properly, users should save the discovered key and use it with the HiddenTear decryptor.
- Download the standalone HiddenTear decryptor.
- Double-click on the hidden-tear-decrypter.exe file to start the tool, enter the key that was discovered by the brute
forcer and click on the Decrypt My Files button. - Once the decryption process has finished, it will display a screen stating how many files were decrypted.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs –HT Brute Forcer, ransomware)
[adrotate banner=”5″] [adrotate banner=”13″]


