
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Steel sheet giant Hoa Sen Group hacked by Maze ransomware operators

Experts at threat intelligence firm Cyble came across a post published by Maze ransomware operators claiming to have breached the steel sheet giant Hoa Sen Group. During the ordinary monitoring of Deepweb and Darkweb, researchers at Cyble came across the leak disclosure post published by the Maze ransomware operators that claim the hack of the Hoa Sen […]

Hoa Sen Group

Experts at threat intelligence firm Cyble came across a post published by Maze ransomware operators claiming to have breached the steel sheet giant Hoa Sen Group.

During the ordinary monitoring of Deepweb and Darkweb, researchers at Cyble came across the leak disclosure post published by the Maze ransomware operators that claim the hack of the Hoa Sen Group.

Hoa Sen Group is the no.1 company in the field of manufacturing and trading steel sheet in Vietnam and the leading exporter of steel sheet in Southeast Asia.

The Hoa Sen Group (HSG) was founded in the year 2001, it has 7,100 employees across all its 343 companies and has been earning annual revenue of around $1.18 billion.

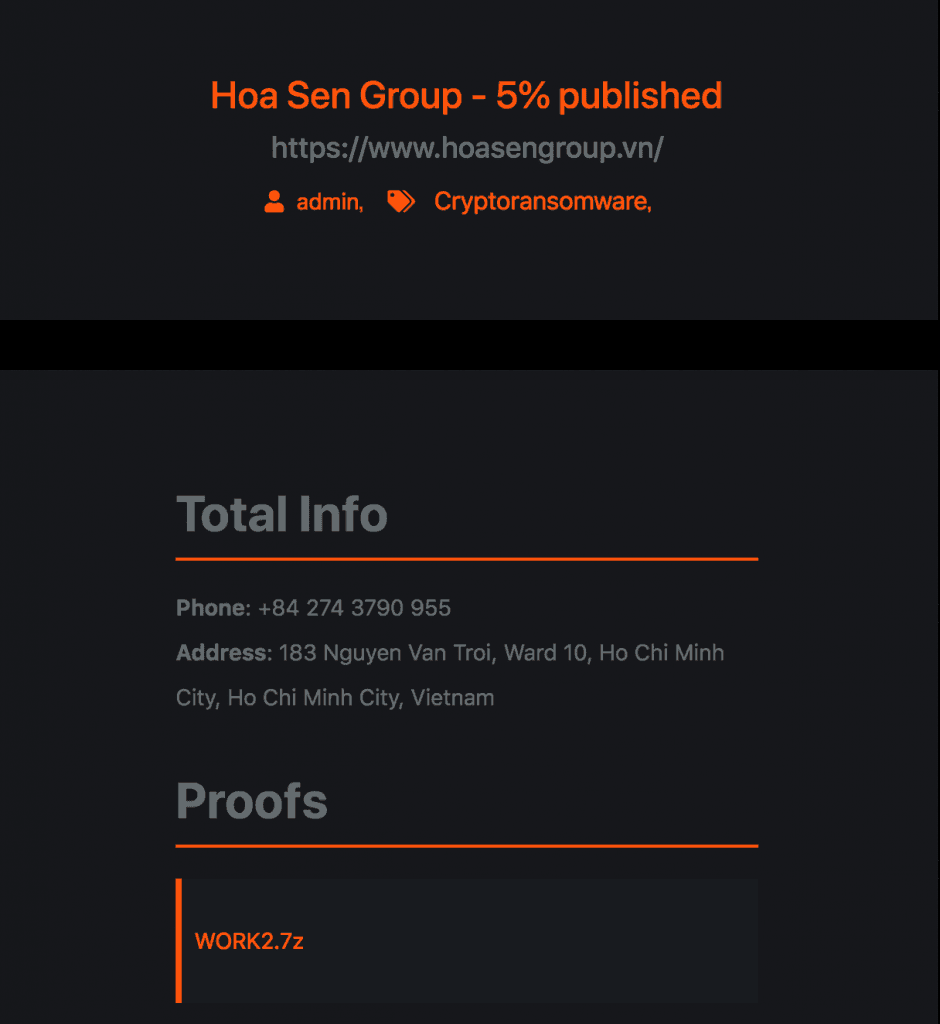
Maze ransomware operators claim to be in possession of the company’s sensitive data and are threatening to release it. Below a snapshot of the leak post published by the Maze Ransomware Operators:

Hoa Sen Group

Experts from Cyble analyzed the leaked data, an archive containing around 1.64 GB of files that correspond to the 5% of the overall stolen data. Maze ransomware operators have released documents containing data of Hoa Sen Group employees (i.e. offer letters released by the company). The archive also includes photos of people professionally dressed that appear to be employees of the company and resumes, academic documents, identity cards of current employees.

“Currently, the ransomware operators claims to have published 5% of company’s total data leak.” reads the post published by Cyble.

“Cyble has been reporting these data breaches to aware individuals of the risks associated with using online services.”

Below a list of tips provided by Cyble to prevent ransomware attacks:

  • Never click on unverified/unidentified links
  • Do not open untrusted email attachments
  • Only download from sites you trust
  • Never use unfamiliar USBs
  • Use security software and keep it updated
  • Backup your data periodically
  • Isolate the infected system from the network
  • Use mail server content scanning and filtering
  • Never pay the ransom.
[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Maze Ransomware Operators)

[adrotate banner=”5″]

[adrotate banner=”13″]


