
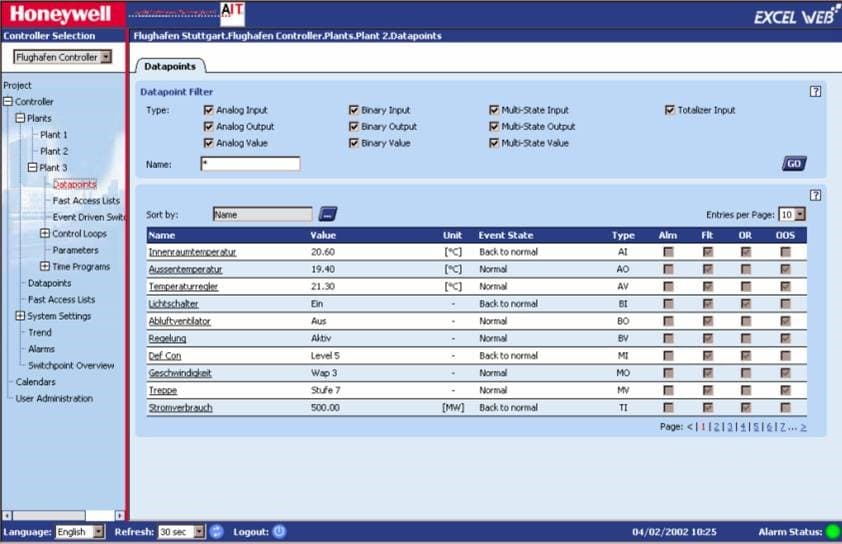
The web-based SCADA system Honeywell XL Web II Controller is affected by multiple flaws that can be remotely exploited to expose passwords in clear text.
A popular web-based SCADA system designed by Honeywell is affected by multiple vulnerabilities that can be remotely exploited to expose passwords in clear text.
In order to access the password in clear text, the attacker just has to access a particular URL to trigger one of the flaws.
The vulnerabilities affect some versions of Honeywell XL Web II controllers, a system that is widely adopted in critical infrastructure across various industries, including energy, wastewater, and manufacturing.

According to the ICS-CERT security advisory, the majority of the affected products is located in Europe and the Middle East.
The Department of Homeland Security’s Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) issued a security advisory to warn of the flaws.
“Independent researcher Maxim Rupp has identified vulnerabilities in Honeywell’s XL Web II controller application.” reads the security advisory. “An attacker may use these vulnerabilities to expose a password by accessing a specific URL. The XL Web II controller application effectively becomes an entry point into the network where it is located.”
ICS-CERT issued advisory ICSA-17-033-01 Honeywell XL Web II Controller Vulnerabilities to ICS-CERT web site https://t.co/2MP0SrajwQ
— ICS-CERT (@ICSCERT) February 2, 2017
#Honeywell XL1000C500 XLWebExe-2-01-00 and prior + XLWeb 500 XLWebExe-1-02-08 and prior.
— Maxim Rupp (@mmrupp) January 6, 2017
The affected products are the Honeywell XL1000C500 XLWebExe-2-01-00 and prior, and XLWeb 500 XLWebExe-1-02-08 and prior.
Honeywell has produced a new version (version 3.04.05.05) to address the vulnerabilities, in order to receive the security updates customers have to contact their local Honeywell Building Solutions branch.
The attacker can also exploit other flaws in the Honeywell XL Web II controllers, he can carry out a path traversal attack by accessing a specific URL, open and change some parameters by accessing a particular URL, or establish a new user session.
The researcher Maxim Rupp that discovered the flaws has detailed them in a blog post recently published.
(Security Affairs – Honeywell XL Web II Controller Vulnerabilities, SCADA)


