
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hostinger disclosed a data breach that affects 14 Million customers

The popular Hosting provider Hostinger disclosed a recent security breach that allowed unauthorized access to a client database. Hostinger, one of the biggest hosting providers, disclosed a recent security breach that allowed attackers to access a client database. The security breach took place on August 23 and may have impacted up to 14 million Hostinger […]

Hostinger notification

The popular Hosting provider Hostinger disclosed a recent security breach that allowed unauthorized access to a client database.

Hostinger, one of the biggest hosting providers, disclosed a recent security breach that allowed attackers to access a client database.

The security breach took place on August 23 and may have impacted up to 14 million Hostinger customers.

“On August 23rd, 2019 we have received informational alerts that one of our servers has been accessed by an unauthorized third party. This server contained an authorization token, which was used to obtain further access and escalate privileges to our system RESTful API Server*. This API Server* is used to query the details about our clients and their accounts.
*[Latest Edit on 2019-08-25 17:43 UTC]” reads the
announcement published by the company.

“The API database, which includes our Client usernames, emails, hashed passwords, first names and IP addresses have been accessed by an unauthorized third party. The respective database table that holds client data, has information about 14 million Hostinger users.

The attackers have compromised an internal server, where they found an authorization token for an internal API, then used the token to access customers’ information via API calls.

Exposed data included Hostinger usernames, hashed passwords (SHA1), customers’ IP addresses, first and last names, and contact information (i.e. Phone numbers, emails, and home addresses). According to Hostinger, financial data were not exposed in the attack.

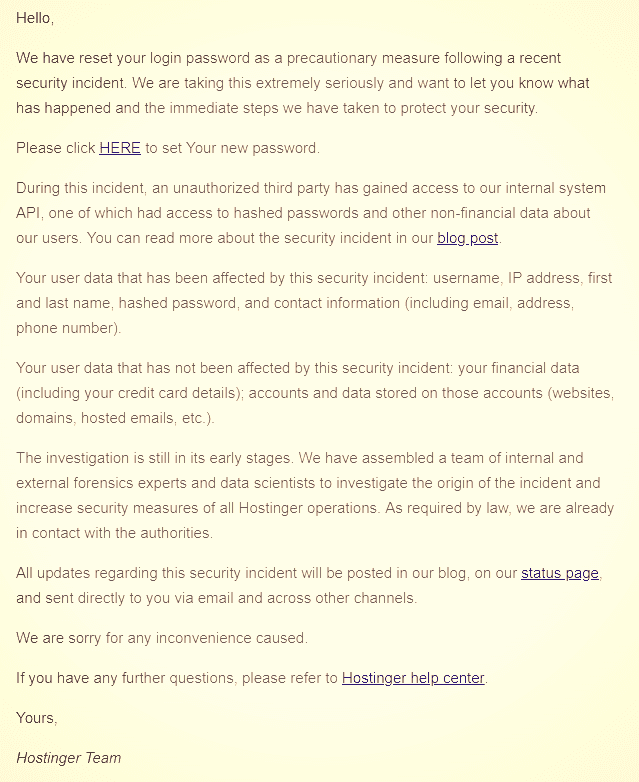
In response to the incident, the company reset passwords for all impacted customers, Hostinger clients received the following notification and instructions on how to access their account again.

Hostinger notification

“We have reset all Hostinger Client passwords as a precautionary measure following a recent security incident.” reads the data breach notification published on the company website. “During this incident, an unauthorized third party has gained access to our internal system API, one of which had access to hashed passwords and other non-financial data about our customers.”

The company determined the affected system and locked out the attackers, the provider has immediately taken down the breached server and the abused API.

At the time of writing, the company is investigating the incident with the help of a team of external forensic experts, it also reported the hack to the authorities.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Hostinger, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


