
The number HTTPs Phishing sites continues to increase, it is the response of phishers to the improvements implemented by Browser-makers.
If you believe that the HTTPs could protect you from phishing attacks you are wrong, in 2014 TrendMicro warned of the increase in the number of HTTPS phishing sites.
After more than two years the situation is going works despite the efforts of Browser-makers to implement warning and alerting systems in their software when users are accessing non-secure websites.
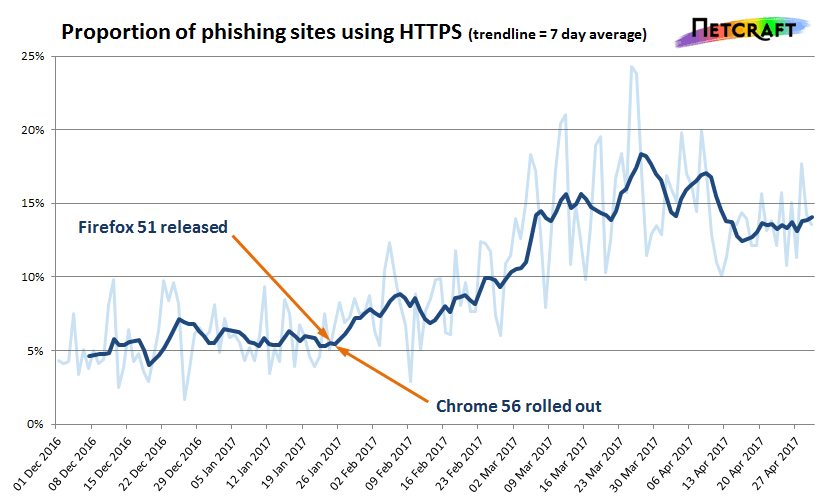
Security researchers at Netcraft have analyzed phishing sites in the wake of Chrome 56 and Firefox 51 adding warnings about insecure sites that request user’s sensitive data (i.e. login credentials).
The data collected by the company shows that cyber criminals are improving their campaigns by adding HTTPS to their phishing websites.
In the following graph is reported the proportion of phishing sites using HTTPS, it is evident the trend despite the countermeasures adopted by Browser-makers.
“However, fraudsters may have quickly realised this, as there has been a dramatic increase in the number of phishing sites making use of HTTPS. If the new browser behaviour has driven this change — and the timing suggests it might have — then it may have also had the unintended side effect of increasing the efficacy of some phishing sites. Phishing sites that now use HTTPS and valid third-party certificates can appear more legitimate, and therefore increase the likelihood of snaring a victim.” reads the analysis published by Netcraft.

Experts formulated another plausible hypothesis for the above increase. The number of websites using HTTPs is increasing and at the same time, phishing prefers to host their malicious content on compromised HTTPs websites.
“Another plausible hypothesis is that many legitimate websites have migrated to HTTPS in response to the new behaviour in Firefox and Chrome. Phishing sites are often hosted on compromised websites, and so this would naturally cause the number of HTTPS phishing sites to increase accordingly; or it could be that some fraudsters are now targeting HTTPS websites in preference to HTTP sites.” continues the analysis.
While most of the phishing sites still use the unencrypted HTTP protocol, it is easy to predict a spike in HTTPS phishing sites over in the next months.
“Regardless of what caused this change, phishing sites that use the unencrypted HTTP protocol could still prove effective against some victims, as not all browsers share the behaviour implemented in Firefox and Chrome. In particular, Microsoft’s Internet Explorer and Edge browsers do not yet display any warnings when users interact with insecure forms.” concludes Netcraft.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – HTTPs phishing, cybercrime)
[adrotate banner=”13″]


