
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Bad actor sells Huiying Medical Technology’s source code for AI-assisted COVID-19 detection

Experts from Cyble identified a threat actor attempting to sell Huiying Medical Technology’s source code for AI-assisted COVID-19 detection and experimental data. Researchers from the data breach notification firm Cyble have identified a credible bad actor that goes online with moniker ‘THE0TIME’ claiming to have gained access to Huiying Medical Technology’s COVID-19 detection’s technology. “As part of […]

Huiying Medical Technology covid19

Experts from Cyble identified a threat actor attempting to sell Huiying Medical Technology’s source code for AI-assisted COVID-19 detection and experimental data.

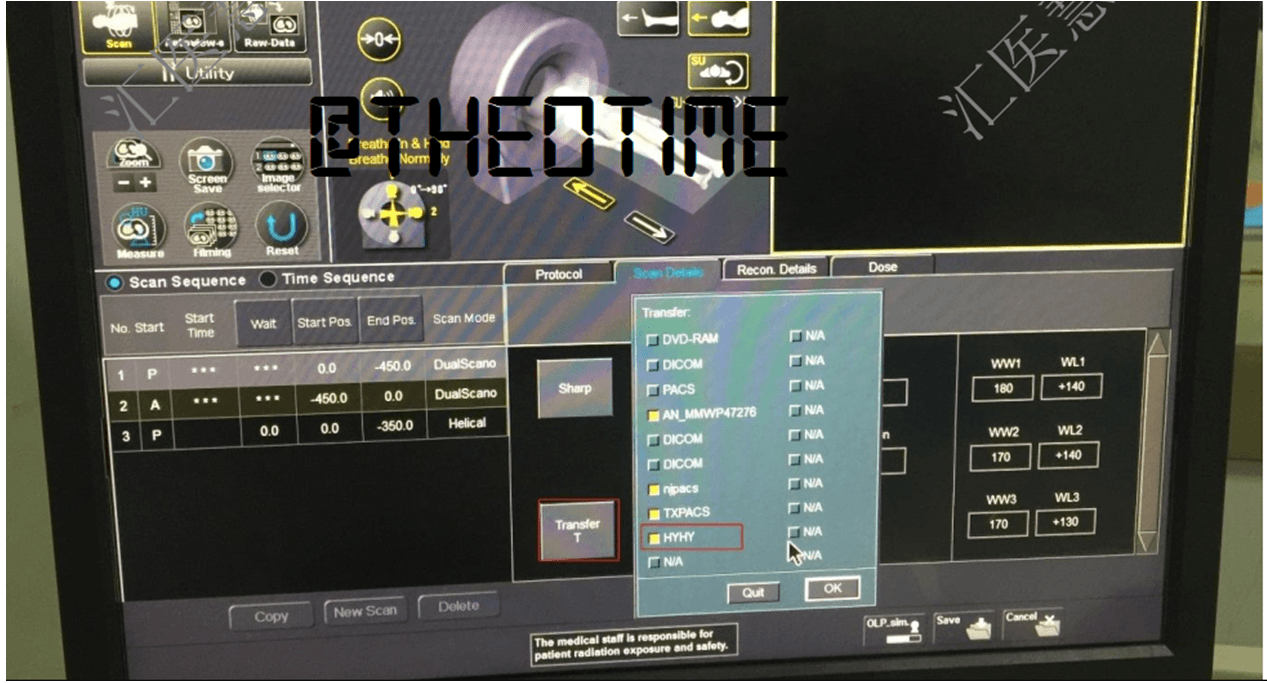
Researchers from the data breach notification firm Cyble have identified a credible bad actor that goes online with moniker ‘THE0TIME’ claiming to have gained access to Huiying Medical Technology’s COVID-19 detection’s technology.

https://twitter.com/AuCyble/status/1253916414504775681

“As part of the breach, the preparator claims to have gained access to the COVID-19 detection technology code, as well as COVID-19 experiments data as well. The price for sale is 4 BTC.” reads a post published by Cyble on Medium.

Huiying Medical Technology (Beijing) Co., Ltd. researches, develops, manufactures, and distributes medical imaging devices.

Huiying Medical Technology developed an AI-based system that can detect suspected contours of pneumonia from CT Chest DICOM images and identify the symptoms of a COVID-19 infection. Huawei, which partners with Huiying, currently sells the system for USD $50,000 per month.

The threat actors are offering for sale the source code for AI-assisted COVID-19 detection and experimental data

THE0TIME is offering the stolen data for sale at 4 BTC, the dump includes:

  • Users — 1.5 MB
  • Technology + source code — 1GB
  • Knowledge for Covid-19 Experiments information — 150 MB
Huiying Medical Technology covid19

Cyble offers data breach monitoring services through the platform http://amibreached.com.

Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Facebook, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


