
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Hacking

iDict, a tool that can break into any iCloud account is available online

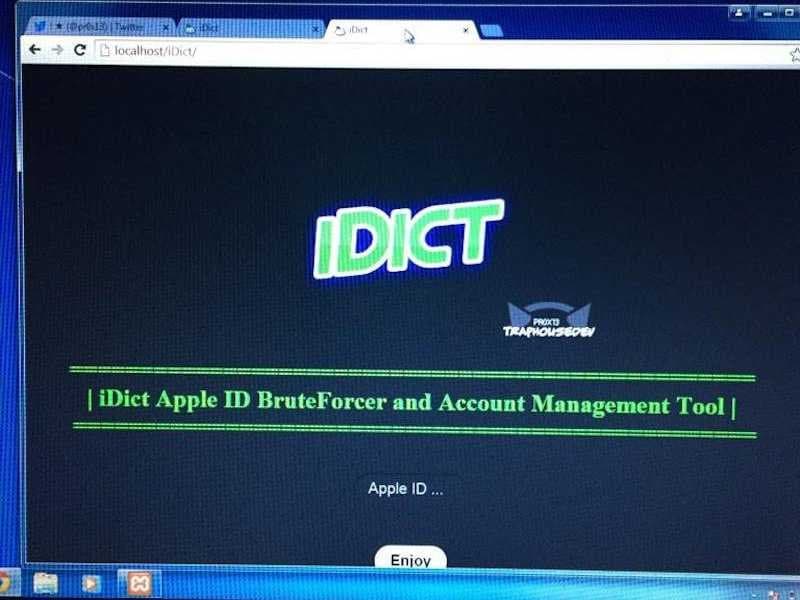
iDict is the a hacking tool that was published on GitHub and that can break into any iCloud account running an Apple ID Dictionary attack. A hacker has released a tool called iDict that he sustains that could be used to break into any iCloud account. According to the expert, iDict implements an exploit that is able […]

iDict, a tool that can break into any iCloud account is available online

iDict is the a hacking tool that was published on GitHub and that can break into any iCloud account running an Apple ID Dictionary attack.

A hacker has released a tool called iDict that he sustains that could be used to break into any iCloud account. According to the expert, iDict implements an exploit that is able to bypass restrictions countermeasures designed by Apple to prevent account hacking.

The user Pr0x13 posted the code of iDict on GitHub, Pr0x13 explains that the code is very easy to use and exploits a very simple mechanism implemented to protect the iCloud accounts. Below an excerpt from the iDict page.

What is this? A 100% Working iCloud Apple ID Dictionary attack that bypasses Account Lockout restrictions and Secondary Authentication on any account.

What this isn’t: A bypass or fully automated removal

Why? This bug is painfully obvious and was only a matter of time before it was privately used for malicious or nefarious activities, I publicly disclosed it so apple will patch it.

iDict PAge

Basically, the tool run a dictionary attack on iCloud Apple ID that bypasses account lockout restrictions and secondary authentication on any account.

The disclaimer explains that the usage of the tool for hacking into iCloud account is illegal, @Pr0x13 decline any responsibility for damages caused by the iDict tool and confirm that he hasn’t broken any account.

“I Didn’t exploit any accounts while writing this, as well i didn’t even test it out (Hope it works lol). I merely observed and reported.”states @Pr0x13

In time I’m writing the unique confirmation on the efficiency of iDict is provided by Twitter and Reddit users which are claiming to have successfully tested it.

idict 2


According to Pr0x13, iDict is able to guess passwords over and over avoiding to be blocked by countermeasures implemented by Apple, it is also able to bypass the two-factor authentication (aka two-step verification)mechanism implemented by Apple to allow users the verification of login attempts. iDict just requires its users to know the email address associated with the targeted iCloud account before it tries to break into it.

If iDict works as explained, the unique possibility for the iCloud users to defend their account is to avoid to share online their email address.

Is this the right time for a new series of Fappening cases?

Pierluigi Paganini

(Security Affairs –  iDict, iCloud hacking)

[adrotate banner=”9″]


