
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Indian foreign ministry’s Global Pravasi Rishta portal leaks expat passport details

The Cybernews research team reported that India’s government platform Global Pravasi Rishta Portal was leaking sensitive user data. Original post @ https://cybernews.com/security/indias-foreign-ministry-leaks-passport-details/ The Global Pravasi Rishta Portal, India’s government platform for connecting with its overseas population, leaked sensitive data, including names and passport details. The Cybernews research team has been alerted that the Global Pravasi […]

Global Pravasi Rishta

The Cybernews research team reported that India’s government platform Global Pravasi Rishta Portal was leaking sensitive user data.

Original post @ https://cybernews.com/security/indias-foreign-ministry-leaks-passport-details/

The Global Pravasi Rishta Portal, India’s government platform for connecting with its overseas population, leaked sensitive data, including names and passport details.

The Cybernews research team has been alerted that the Global Pravasi Rishta Portal was leaking sensitive user data. Unfortunately, the tip proved accurate.

The platform exposed user names, surnames, country of residence, and email addresses in plaintext, as well as occupation status, phone and passport numbers. The leak was possible because of poor security measures, such as a lack of authentication methods.

The Global Pravasi Rishta Portal is a platform with the goal of connecting 30 million Indian expats. The platform owner is the Ministry of External Affairs of India, the country’s government body responsible for implementing foreign policy.

The portal is meant as a tool for communication between the Ministry of External Affairs, Indian Missions, and the Indian diaspora. Pravasi Rishta means “expatriate relationships” in English.

The Cybernews team has reached out to the Ministry of External Affairs to inform it of the leak. We did not receive a reply, but several days later the security issue had been fixed.

Global Pravasi Rishta

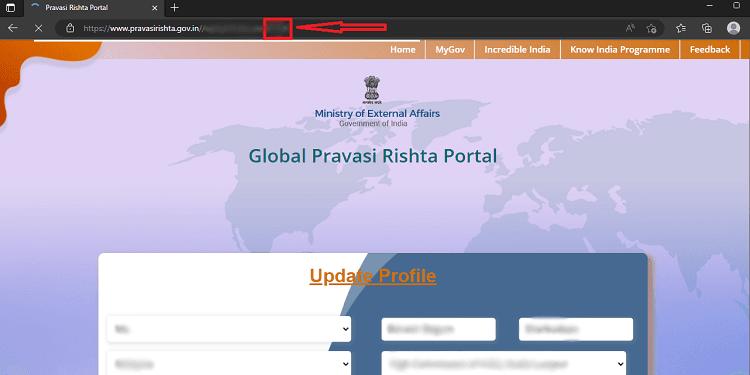
The data was exposed via the website’s edit function, where manipulating the URL allowed anyone to access the edit details of any user on the site. In other words, it takes only one registered user to access all of them, since changing the user ID in the URL leads to another user’s account.

If you want to know which is the risk for the exposure of passport numbers read the original post published by CyberNews @https://cybernews.com/security/indias-foreign-ministry-leaks-passport-details/.

About the author: Vilius Petkauskas, Senior Journalist ay CyberNews 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Global Pravasi Rishta)

[adrotate banner=”5″]

[adrotate banner=”13″]


