
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Personal details and documents for millions of Indians available in the deep web

Researchers have discovered a dump containing 29.1M Indian jobseekers personal details that was offered for free in the hacking underground. Researchers discovered a dump containing 29.1M Indian jobseekers personal details that was offered for free in the hacking underground. An anonymous entity told Cyble researchers that the data were stored on an unprotected elastic search […]

Indian Identity card leak

Researchers have discovered a dump containing 29.1M Indian jobseekers personal details that was offered for free in the hacking underground.

Researchers discovered a dump containing 29.1M Indian jobseekers personal details that was offered for free in the hacking underground.

An anonymous entity told Cyble researchers that the data were stored on an unprotected elastic search instance that is no longer accessible.

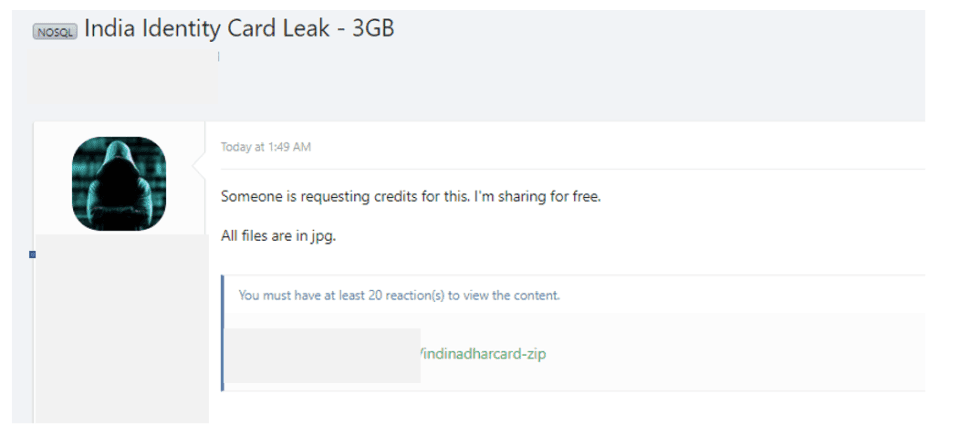
While Cyble was investigating the issue, a threat actor published more than 2,000 Indian Identity cards (Aadhaar cards) on one hacking forum, files appears to have originated from 2019.

Indian Identity card leak

Then the threat actor leaked 1.8M identity cards belonging to citizens of the Madhya Pradesh state on their forum.

“Cyble has indexed this information on their data breach monitoring and notification platform, Amibreached.com. People who are concerned about their information leakage, can ascertain the risks by registering to the platform.” reads the post published by Cyble.

Cyble researchers also discovered that a threat actor posted 2.3 GB (zipped) file on one of the hacking forums.

This time the leak contains a lot of personal details of millions of Indians Job seekers from different states. At the time of writing this article, the experts are still investigating the source of the leak.

“It appears to have originated from a resume aggregator given the sheer volume and detailed information.” state the experts.

“Cyble researchers have identified a sensitive data breach on the darkweb where an actor has leaked personal details of ~29 Million Indian Job Seekers from the various states. The original leak appears to be from a resume aggregator service collecting data from various known job portals. Cyble’s team is still investigating this further and will be updating their article as they bring more facts to the surface. This breach includes sensitive information such as email, phone, home address, qualification, work experience etc.”

Crooks could use personal information exposed in both data leaks to conduct various malicious activities, including identity thefts, scams, and corporate espionage.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Indians data leaks, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


