
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

InnfiRAT Trojan steals funds from Bitcoin and Litecoin wallets

Researchers at Zscaler have spotted a new malware dubbed InnfiRAT that infects victims’ systems to steal cryptocurrency wallet data.  Researchers at Zscaler have discovered a new Trojan dubbed InnfiRAT that implements many standard Trojan capabilities along with the ability to steal cryptocurrency wallet data.  “As with just about every piece of malware, InnfiRAT is designed […]

Bitcoin

Researchers at Zscaler have spotted a new malware dubbed InnfiRAT that infects victims’ systems to steal cryptocurrency wallet data. 

Researchers at Zscaler have discovered a new Trojan dubbed InnfiRAT that implements many standard Trojan capabilities along with the ability to steal cryptocurrency wallet data. 

“As with just about every piece of malware, InnfiRAT is designed to access and steal personal information on a user’s computer.” states a blog post published by Zscaler. “Among other things, InnfiRAT is written to look for cryptocurrency wallet information, such as Bitcoin and Litecoin. InnfiRAT also grabs browser cookies to steal stored usernames and passwords, as well as session data.”

Upon execution, the malware initially checks whether the file is executing from %AppData% directory or not with the name NvidiaDriver.exe. The malware then checks for network connectivity by making a request to “iplogger[.]com/1HEt47,” and records all the running processes in an array to check whether any of them is running with the name NvidiaDriver.exe. If it finds one of the processes running with this name, it kills that process and waits for an exit.

The malicious code will make a copy of itself in the AppData directory before writing a Base64 encoded PE file in memory to execute the main component of the Trojan. 

As the execution of the malware starts, it checks for the presence of virtualized environment that could be used by researchers to analyze the threat. If the malware is not running in a sandbox it will contact the command-and-control (C2) server, transfer the information stolen form the machine, and await further commands.

The InnfiRAT Trojan can also deploy additional payloads to steal files, capture browser cookies to harvest stored credentials for various online services and grab open sessions. The malware is also able to shut down traditional antivirus processes.

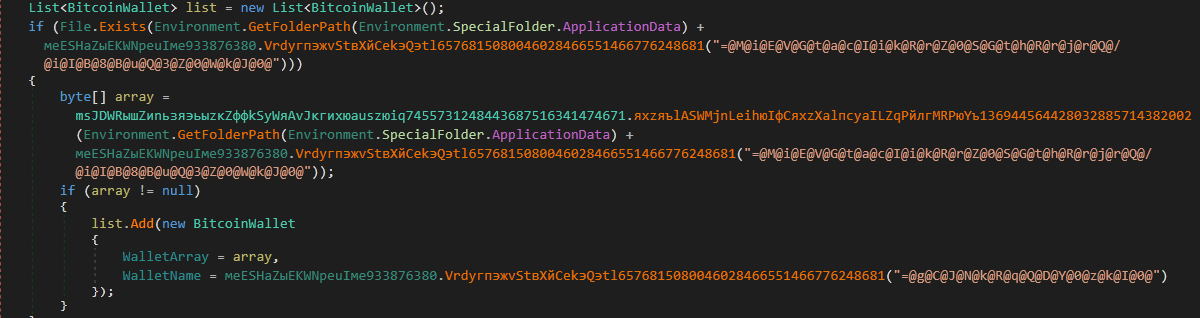
InnfiRAT scans the machine for files associated with Bitcoin (BTC) and Litecoin (LTC) wallets (Litecoin: %AppData%\Litecoin\wallet.dat,
Bitcoin: %AppData%\Bitcoin\wallet.dat), if they are present, the malicious code siphons existing data in the attempt of stealing the victims’ funds.

Bitcoin

“Because RATs are usually downloaded as a result of a user opening an email attachment or downloading an application that has been infected, the first line of defense is often the users who must, as always, refrain from downloading programs or opening attachments that aren’t from a trusted source.” concludes the researchers.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – InnfiRAT, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


