
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

IntelBroker claimed the hack of the Los Angeles International Airport

The popular hacker IntelBroker announced that it had hacked the Los Angeles International Airport by exploiting a flaw in one of its CRM systems. The website Hackread first reported that the popular hacker IntelBroker had breached one of the CRM systems used by the Los Angeles International Airport. IntelBroker announced it had exploited a vulnerability […]

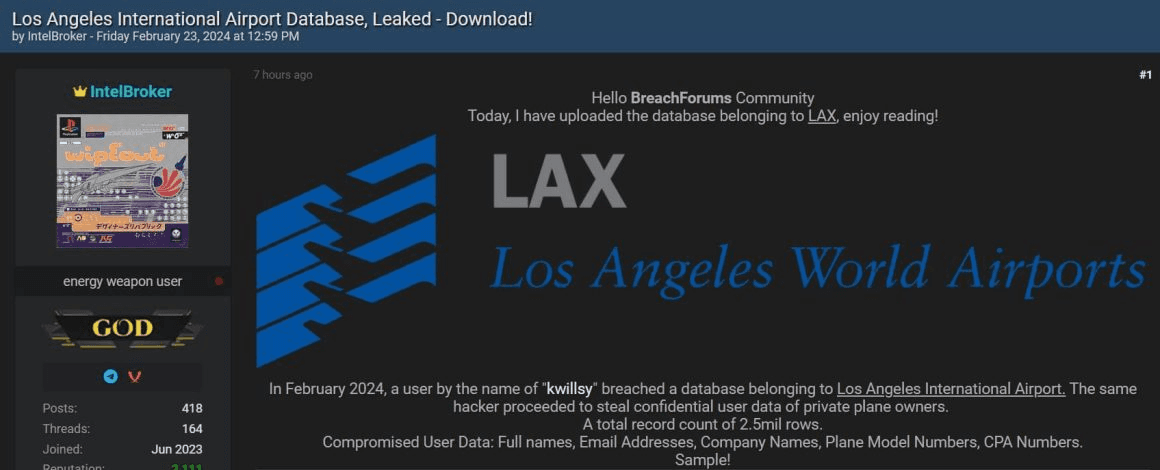
Los Angeles International Airport hack

Screenshot credit: Hackread.com

The popular hacker IntelBroker announced that it had hacked the Los Angeles International Airport by exploiting a flaw in one of its CRM systems.

The website Hackread first reported that the popular hacker IntelBroker had breached one of the CRM systems used by the Los Angeles International Airport. IntelBroker announced it had exploited a vulnerability in the target system, the attack took place this month.

“IntelBroker informed Hackread.com that they successfully executed the data breach by exploiting a vulnerability within one of the CRM systems utilized by the Los Angeles International Airport.” reads the post published by Hackread.

IntelBroker is considered a reputable threat actor, it was linked to the breaches of DC Health Link,d Volvo Cars, and Hewlett Packard Enterprise (HPE). The hacker is also behind a recent leak of the Facebook Marketplace database.

The hacker claims to have gained access to a database containing confidential data of the owners of private planes. The database contained 2.5 million records, containing the following data:

  • Full names
  • CPA numbers
  • Email addresses (1.9 million emails – total 15,8000 emails after removing duplicates).
  • Company names
  • Plane model numbers
  • Tail numbers (Refers to an identification number painted on an aircraft tail).

The security breach did not impact travelers.

IntelBroker announced the hack on BreachForumsm the post states that in February 2024, a user named ‘kwillsy’ breached a database of the Los Angeles International Airport. However, IntelBroker told HackRead that “kwillsy” is not associated with the security breach, and they claimed full responsibility for the data breach.

Los Angeles International Airport hack
Screenshot credit: Hackread.com

HackRead notified the LA Airport.

Follow me on Twitter: @securityaffairs and Facebook

Pierluigi Paganini

(SecurityAffairs – hacking, LA International Airport)


