
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Internal modem can be exploited by malware to gain persistence

Two security experts at the last Def Con hacking conference have demonstrated how Internal LTE/3G modems can be hacked to help malware survive OS reinstalls Many users totally ignore that LTE/3G modems built into new business laptops and tablets have a dedicated processor and operating system that could be exploited by threat actors to maintain persistent […]

Internal modem can be exploited by malware to gain persistence

Two security experts at the last Def Con hacking conference have demonstrated how Internal LTE/3G modems can be hacked to help malware survive OS reinstalls

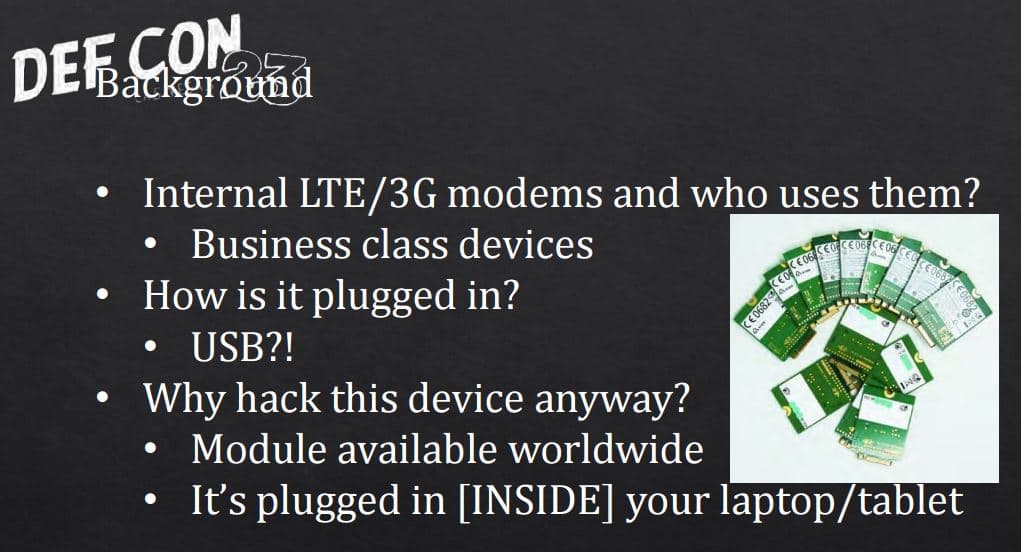
Many users totally ignore that LTE/3G modems built into new business laptops and tablets have a dedicated processor and operating system that could be exploited by threat actors to maintain persistent access to a compromised device.

The security researchers Mickey Shkatov and Jesse Michael from Intel’s security group in a talk at the DEF CON security conference in Las Vegas demonstrated how a malware that infect a machine could rewrite the firmware of a popular Huawei LTE modem.

insecure internal modem LTE talk

The expert explained that Huawei LTE modem runs a Linux-based OS, a modification of the Android OS, and is connected to the host system through an internal USB interface. The use of an internal USB interface means that the module could be used by attackers to emulate a number of devices connected to the primary OS, including keyboard, mouse, CD-ROM drive, network card, or other USB device.

The researchers were able to rewrite the firmware because the update process is weak, in fact, the updates aren’t protected by digital signature neither by encryption mechanisms. The two researchers developed their malicious firmware and served it through the Windows update utility provided by the vendor.

The updates could be served in various ways, by exploiting malicious programs already running on the target machine, or by tricking victims into thinking that they are legitimate security patches.

Once the attacker has rewritten the firmware running on the modem it will be able to maintain the infection even if the host OS is reinstalled. The experts also explained that the malicious firmware could be also instructed to ignore any subsequent firmware update, in this case, the unique way to restore the infected PC is to remove the infected modem module.

Huawei promptly fixed the issue, introducing a secure boot that blocks the flashing of unauthorized firmware images.

The presentation made by the security experts raises the question about the possible exploitation of dedicated processors and operating systems that equip any device connected to a system. Malware authors can exploit them to ensure persistence of their malicious code.

Pierluigi Paganini

(Security Affairs – Internal LTE/3G modems, hacking)


