Microsoft recently issued the patches to fix set of flaws in Internet Explorer, years after their discovery by black-hats in the hacking underground.
Microsoft finally fixed a set of vulnerabilities in Internet Explorer years after they were discovered by black-hats in the hacking underground. I have contacted a black hat in the underground that who made a catastrophic prediction:
“And millions of people affected by it, but most of them still unaware of that they got hacked nearly a year ago” [4]
On September 13, 2016, Microsoft released two major security updates (MS16-105, MS16-104 for Edge and Internet Explorer browsers. [1][2]
The updates address various vulnerabilities rated with a severity level included from “Critical” to “Moderate.” According to ZDI some of these vulnerabilities have been reported to Microsoft on May 2016. Unfortunately evidence suggests that -hopefully- “some of them” has been known since 2014 and has been used in major attacks in the wild, such as the CVE-2016-3351 (creation date is 2016-03-15).
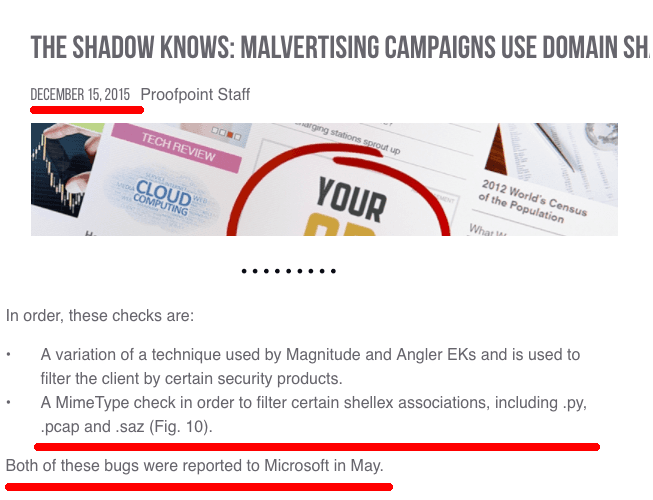
The CVE-2016-3351 flaw allows malicious script to just step back -or filter out- on configurations that are suspected to be on security analysis by checking various file type integrations such as .pcap files which are used to get network packet dumps by various traffic analysis software.
On December 15, Proofpoint has mentioned this vulnerability in its threat-insight blog mentioning Angler EK. [4]

The expert that I have been in touch was claiming that both CVE-2016-3351 and CVE-2016-3295 have been discovered long before their recent disclosure by actors in the underground, but only the CVE-2016-3351 was resolved in public. He also added that actively used CVE-2016-3295 exploit was always confused as CVE-2015-0046 and will be understood shortly. [4]

Hopefully we will get more details as POCs will be provided us.
Stay Tuned!
References
[1] https://technet.microsoft.com/library/security/MS16-105
[2] https://technet.microsoft.com/library/security/MS16-104
[3] https://www.proofpoint.com/uk/threat-insight/post/The-Shadow-Knows
[4] “An underground hacker”
About the Author Harun Esur
 Harun Esur is founder of Sceptive, a security firm specialized on underground cyberwarfare and services for financial companies. Coding, hacking and protecting padawans in cyberworld since the invention of Commodore 64 and VICMODEM model 1600.
Edited by Pierluigi Paganini
(Security Affairs – CVE-2016-3351, exploit)