
The author of an IoT botnet is distributing a backdoor script for ZTE routers that also includes his own backdoor to hack script kiddies
A weaponized IoT exploit script is being used by script kiddies, making use of a vendor backdoor account to hack the ZTE routers. Ironically, this is not the only backdoor in the script. Scarface, the propagator of this code has also deployed his custom backdoor to hack any script kiddie who will be using the script.
With top names in IOT (Paras/Nexus/Wicked) being inactive, Scarface/Faraday is presently a go to name for script kiddies for buying IoT botnet code as well as weaponized exploits. While Scarface mostly has a good credibility, we observed that he has released a weaponized ZTE ZXV10 H108L Router known vulnerability with a backdoor which compromises the system of the script kiddie when they run it.
The vulnerability is a known one and involves the usage of a backdoor account in ZTE Router for login followed a command injection in manager_dev_ping_t.gch. The code by Scarface targets devices on a different port, 8083 though( justifying why our NewSky honeypots are seeing a surge of this vulnerability usage on port 8083 instead of the standard 80/8080 ports). It is, however, not the only difference.

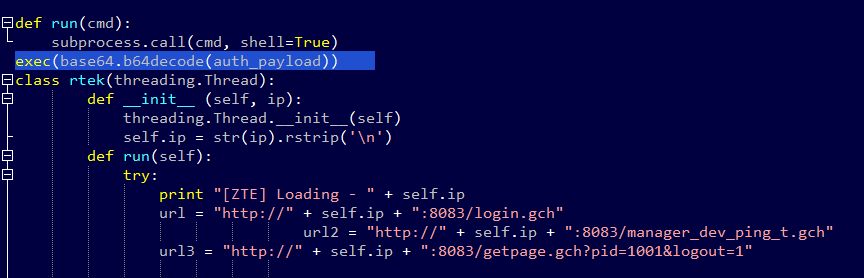
In the leaked code snippet, we see login_payload for the backdoor usage and command_payload for the command injection. However, there is one more variable, auth_payload, which contains Scarface’s backdoor, encoded in base64.
This backdoor code is executed sneakily via exec, separately from the three steps of the actual vulnerability (using the vendor backdoor, command injection and log out) which are shown in the image below:

The backdoor code after decoding connects to another website which has code to connect to a paste(.)ee URL and execute further code:


We can see that a set of backdoor user credentials are added, followed by trace deletion by clearing logs and history. Another URL is connected to via wget which doesn’t do much as it hosts a meme video (probably an indicator that by this time Scarface has owned your device).

Backdooring rival IoT botnet operator can have several purposes. For example, the bigger fish Scarface after controlling the script kiddies systems can also control the smaller botnets they have constructed, or he can simply use access to rival IoT botnet operator systems for personal rivalry /grudges.
About the author Ankit Anubhav (@ankit_anubhav)
Ankit Anubhav Principal Researcher, NewSky Security
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – IoT botnet, backdoor)
[adrotate banner=”5″]
[adrotate banner=”13″]


