
Microsoft researchers reported that Iranian cyber espionage group MuddyWater is exploiting the Zerologon vulnerability in attacks in the wild.
Microsoft published a post and a series of tweets to warn of cyber attacks exploiting the Zerologon vulnerability carried out by the Iran-linked APT group known as MuddyWater, aka Mercury.
The Zerologon vulnerability, tracked as CVE-2020-1472, is an elevation of privilege that resides in the Netlogon. The Netlogon service is an Authentication Mechanism used in the Windows Client Authentication Architecture which verifies logon requests, and it registers, authenticates, and locates Domain Controllers.
An attacker could exploit the vulnerability to impersonate any computer, including the domain controller itself, and execute remote procedure calls on their behalf.
An attacker could also exploit the flaw to disable security features in the Netlogon authentication process and change a computer’s password on the domain controller’s Active Directory.
The only limitation on how to carry out a Zerologon attack is that the attacker must have access to the target network.
Administrators of enterprise Windows Servers have to install the August 2020 Patch Tuesday to mitigate “unacceptable risk” posed by the flaw to federal networks.
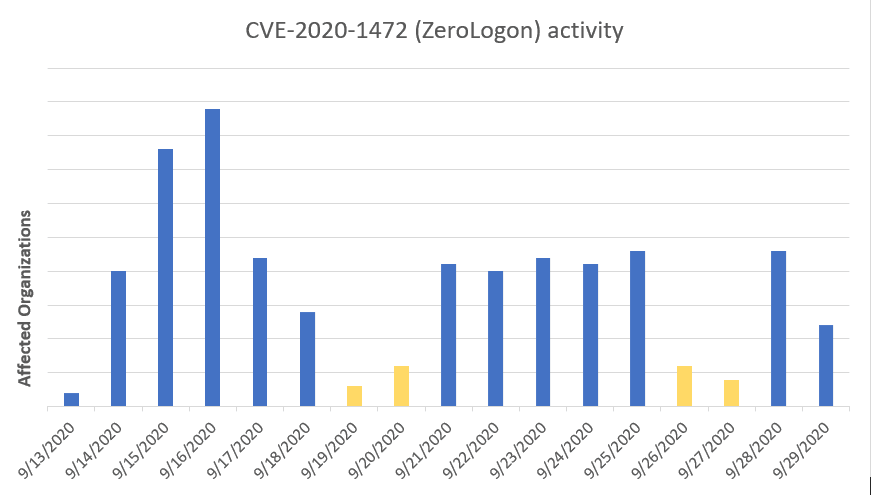
According to Microsoft’s Threat Intelligence Center (MSTIC) the attacks exploiting this vulnerability surged since September 13.

“One of the adversaries noticed by our analysts was interesting because the attacker leveraged an older vulnerability for SharePoint (CVE-2019-0604) to exploit remotely unpatched servers (typically Windows Server 2008 and Windows Server 2012) and then implant a web shell to gain persistent access and code execution.” reads the analysis published by Microsoft. “Following the web shell installation, this attacker quickly deployed a Cobalt Strike-based payload and immediately started exploring the network perimeter and targeting domain controllers found with the ZeroLogon exploit.”
Microsoft linked the attacks to the Iranian cyberespionge group MERCURY, also known as MuddyWater, SeedWorm and TEMP.Zagros.
The first MuddyWater campaign was observed in late 2017 when targeted entities in the Middle East.
The experts called the campaign ‘MuddyWater’ due to the confusion in attributing a wave of attacks that took place between February and October 2017 targeting entities in Saudi Arabia, Iraq, Israel, United Arab Emirates, Georgia, India, Pakistan, Turkey, and the United States to date.
The group evolved over the years by adding new attack techniques to its arsenal.
Microsoft publicly shared some file indicators for the attacks along with variations of the ZeroLogon exploits its experts have detected. Many of these exploits were recompiled versions of well-known, publicly available proof-of-concept code. Microsoft pointed out that MS Defender for Endpoint can also detect certain file-based versions of the CVE-2020-1472 exploit when executed on devices protected by Microsoft Defender for Endpoints.
The MuddyWater attackers have begun around one week after the first proof-of-concept code was published, and Microsoft began detecting the first Zerologon exploitation attempts.
At the time, the Department of Homeland Security’s CISA issued an emergency directive to order government agencies to address the Zerologon vulnerability (CVE-2020-1472) by Monday, September 21.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Zerologon)
[adrotate banner=”5″]
[adrotate banner=”13″]


