
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

New DDoS IRC Bot distributed through Korean webHard platforms

Researchers spotted an IRC bot written in GoLang that is being used to carry out DDoS attacks targeting users in Korea. Researchers from AhnLab’s Security Emergency-response Center (ASEC) spotted an IRC bot written in GoLang that is being used to carry out DDoS attacks targeting users in Korea. Vxers use GoLang because it is easy and allows the development […]

DDoS IRC Bot

Researchers spotted an IRC bot written in GoLang that is being used to carry out DDoS attacks targeting users in Korea.

Researchers from AhnLab’s Security Emergency-response Center (ASEC) spotted an IRC bot written in GoLang that is being used to carry out DDoS attacks targeting users in Korea.

Vxers use GoLang because it is easy and allows the development of cross-platform malicious codes.

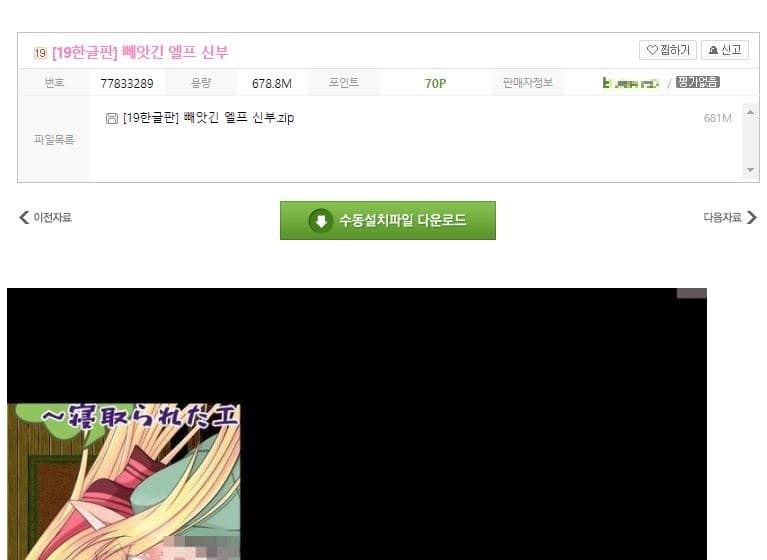
The DDoS IRC Bot strains are disguised as adult games and are being installed via platforms commonly used for the distribution of malware in Korea, so-called webhards. Webhards were also used in past campaigns to distribute njRAT and UDP Rat.

The attack chain starts with threat actors uploading malware disguised as an adult game to the webhard. Attackers used different games containing the same malware. The malicious code is hosted on a web hard drive or a remote file hosting service in the form of compressed ZIP archives. Upon executing the executable (“Game_Open.exe”) in the archive, the malware is executed while the actual game is launched.

DDoS IRC Bot

This downloader connects to a remote command-and-control (C&C) server to retrieve additional payloads, including an IRC bot that can perform DDoS attacks.

“But “Game_Open.exe” is not a launcher that runs the game. It is an executable that runs the additional malware. To be more precise, it changes the “PN” file existing in the same path as “scall.dll” and runs it. Then it copies the original game executable “index” to “Game.exe” to run it. As such, users would assume that the game is being run normally.” reads the analysis published by ASEC. “It is also a type of DDoS Bot malware, but it uses IRC protocols to communicate with the C&C server.Unlike UDP Rat that only supported UDP Flooding attacks, it can also support attacks such as Slowloris, Goldeneye, and Hulk DDoS.”

Once executed, the Golang DDoS IRC Bot connects to a particular IRC server and enters the attacker’s c in order to receive commands, including one that can instruct the bot to perform DDoS attacks.

The report published by ASEC also includes indicators of compromise for this threat.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, DDoS)

[adrotate banner=”5″]

[adrotate banner=”13″]


