
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Is the North Korea behind the attack on the Seoul Subway Operator?

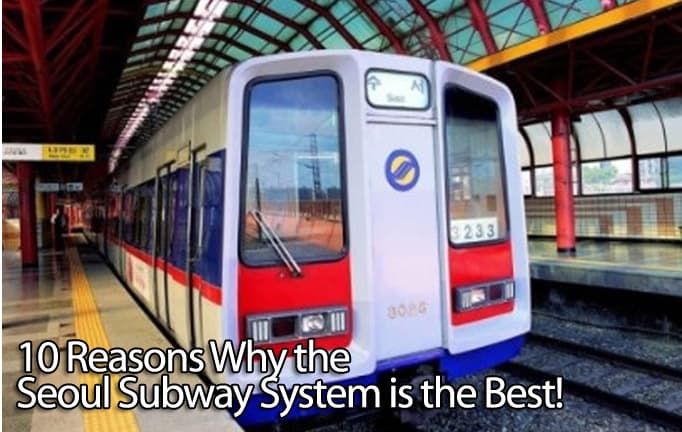
According to the Government of Seoul, the North Korea is the main suspect for a cyber attack that last year hit the South Korean capital’s subway system. The attack, staged between March and August 2014, affected several servers of Seoul Metro, which runs four major subway lines, According to the ruling party legislator Ha Tae-Kyung […]

Is the North Korea behind the attack on the Seoul Subway Operator?

According to the Government of Seoul, the North Korea is the main suspect for a cyber attack that last year hit the South Korean capital’s subway system.

The attack, staged between March and August 2014, affected several servers of Seoul Metro, which runs four major subway lines,

According to the ruling party legislator Ha Tae-Kyung the North Korea is responsible of a cyber attack on the subway system in Seoul. Intelligence reports revealed that the cyber attack has been carried out last year between March and August 2014  and affected a number of servers of South Corean capital ‘s Metro. The Seoul’s subway lines are among the most crowded in the world, is has been estimated that it carries around 5.25 million passengers a day.

Ha Tae-Kyung revealed that nearly 60 employee computers were infected by malware, the experts at the National Intelligence Service (NIS) that analyzed the malicious code have found many similarities to those North Korean hackers have used in precedent attacks.

Seoul Metro Subway North Korea hack 2

A spokesman for the Seoul Metro confirmed the cyber attack, but clarified that computers used for the direct operation of Metro were not compromised by the hackers.

“There were data and information leaks, but none related to direct operations,” said the spokesman.”We still don’t know who was behind the attack,” he added.

According to the Government of Soul, the North Korean cyber army has targeted numerous targets in the South, including banks, government agencies, military and TV broadcasters.

In December a cyber attack hit a nuclear power plant operator in South Korea, also in that circumstance the Government of Seoul blamed Pyongyang, that anyway denied any involvement.

South Korea is investing to improve its cyber capabilities, earlier 2014, the Yonhap news agency revealed that the South Korea, inspired by Stuxnet, was planning to create and use a cyber weapon. The plans are dated 2010 and were proposed to the Government on February 19th.

The South Korea was working on the development of a cyber weapon to hit nuclear facilities in the North, in response to the intensification of the North in the testing of nuclear weapons conducted in underground with controlled explosions.

Pierluigi Paganini

(Security Affairs – North Korea, hacking)


