
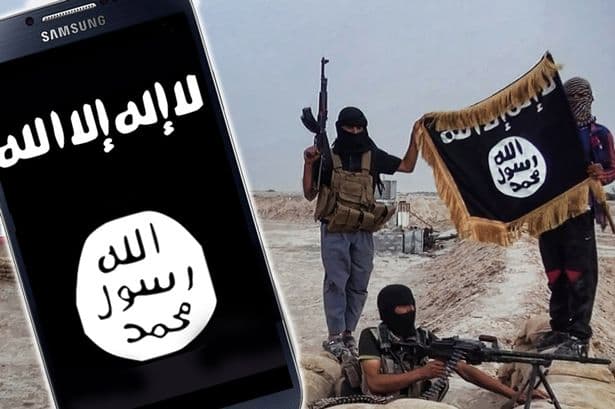
Ghost Security Group has reportedly discovered an Android mobile application used by members of the ISIS organization for secure communications.
According to the Christian Science Monitor, the Ghost Security Group has reportedly discovered an Android mobile app used by members of the ISIS organization.
The Ghost Security Group is the notorious group of cyber experts in counter-terrorism networks that is involved in a series of initiatives against the ISIS radical group online.
In July, the group has supported US law enforcement and Intelligence agencies in thwarting ISIS terror plots in New York and Tunisia.
The Android app discovered by the experts is spread through hidden channels in popular messaging apps like Telegram. The ISIS members have developed the app as an alternative communication channel, the mobile application is reportedly used to spread propaganda and share information on the operations of the group.
“They want to create a broadcast capability that is more secure than just leveraging Twitter and Facebook,” Ghost Security Group chief operating officer Michael Smith II told the Christian Science Monitor. “Increasingly what you will see is the focus on developing means to control the distribution of their materials on a global scale.”
The discovery made by the Ghost Security Group demonstrates the cyber capabilities of the group, abilities that were discussed in the past by prominent experts, including the F-Secure Chief Research Officer Mikko Hypponen.
The popular expert said he worries about cyber extremists that could penetrate critical infrastructure and cause serious damages. The expert explained that the ISIS is probably the first group of terrorist that has hacking capabilities to manage a major attack against a government infrastructure, and the situation is getting worse because this group is gaining greater awareness of the effectiveness of an offensive launched by the cyberspace.
“The Islamic State is the first extremist group that has a credible offensive cyber capability,” said F-Secure Chief Research Officer Hyppönen, speaking last week at the Wall Street Journal’s WSJDLive conference in Laguna Beach, Calif. “Clearly, this situation isn’t getting better. It’s getting worse.”
In this period the US Congress is discussing the role of encryption in commercial products and services, and their potential abuse made by radical groups.

Intelligence agencies and law enforcement bodies worldwide claim that terrorists have exploited encryption implemented in commercial communications platform to arrange terrorist attacks, including the one that hit Paris on November, 13.
In August, a US security consultancy discovered another app dubbed Nasher developed by the member of the ISIS. Also in that case, the Android app was spread through unofficial channels. Users were required to download a special code shared among jihadist online communities and install the app on their device manually.
Islamic State uses the app – which it calls Nasher – to catalogue written reports, radio news and video files.
At the time of writing, the landing page for the app’s APK (Android application package) file had been viewed over 7,500 times although there’s no telling how many downloads have been made.

[adrotate banner=”9″]
(Security Affairs – ISIS, terrorism, mobile app)
[adrotate banner=”13″]


